A sovereign communications platform gives your organisation control over where its communications data lives, who can access it, and how it is protected. Getting that right matters more than it appears.
Sovereignty in communications comes down to one thing: being in charge of your own data. Organisations manage that control in different ways. Some run their communications on managed sovereign cloud infrastructure, where environments are governed under EU law and designed to meet specific regulatory requirements. Others require on-premises or air-gapped deployments, where the organisation holds full control over hardware and software with no external dependencies and no third-party pathway to the data.
Two properties must hold regardless of which deployment approach your organisation chooses.
- Data sovereignty means your messages, voice traffic, and files are stored and processed within a designated geographic region or jurisdiction: inside the EU, within national territory, or inside your own infrastructure.
- Technical sovereignty means you always have access to your own communications data, and no vendor controls it. A platform where a provider can be compelled by a foreign government to access your data in readable form, or one that can cut off your access by changing its terms, fails the second test regardless of where its servers are located.
Most regulated organisations need both. Which deployment approach fits depends on their operational requirements, regulatory context, and threat model.
Evaluating a sovereign communications platform starts with understanding which approach your environment requires.
01How organisations manage sovereignty in communications
Organisations achieve communications sovereignty in different ways, and each approach serves a legitimate operational purpose.
At the managed end, cloud environments designed to meet EU data residency, jurisdictional, and operational transparency requirements give organisations regulatory compliance without the overhead of running their own hardware. For organisations that need to scale quickly, meet NIS2 or DORA requirements, and handle workloads that do not demand full physical isolation, this tier is fit for purpose. It is a deliberate architectural decision, not a compromise.
At the isolated end, on-premises and air-gapped environments give organisations full control over the hardware and software stack, with no external dependency and no third party with any pathway to the data. This is the right architecture for defence operations, classified programmes, and critical national infrastructure where even a well-governed cloud environment introduces unacceptable risk. Not because cloud is inherently untrustworthy, but because the threat model demands something different.
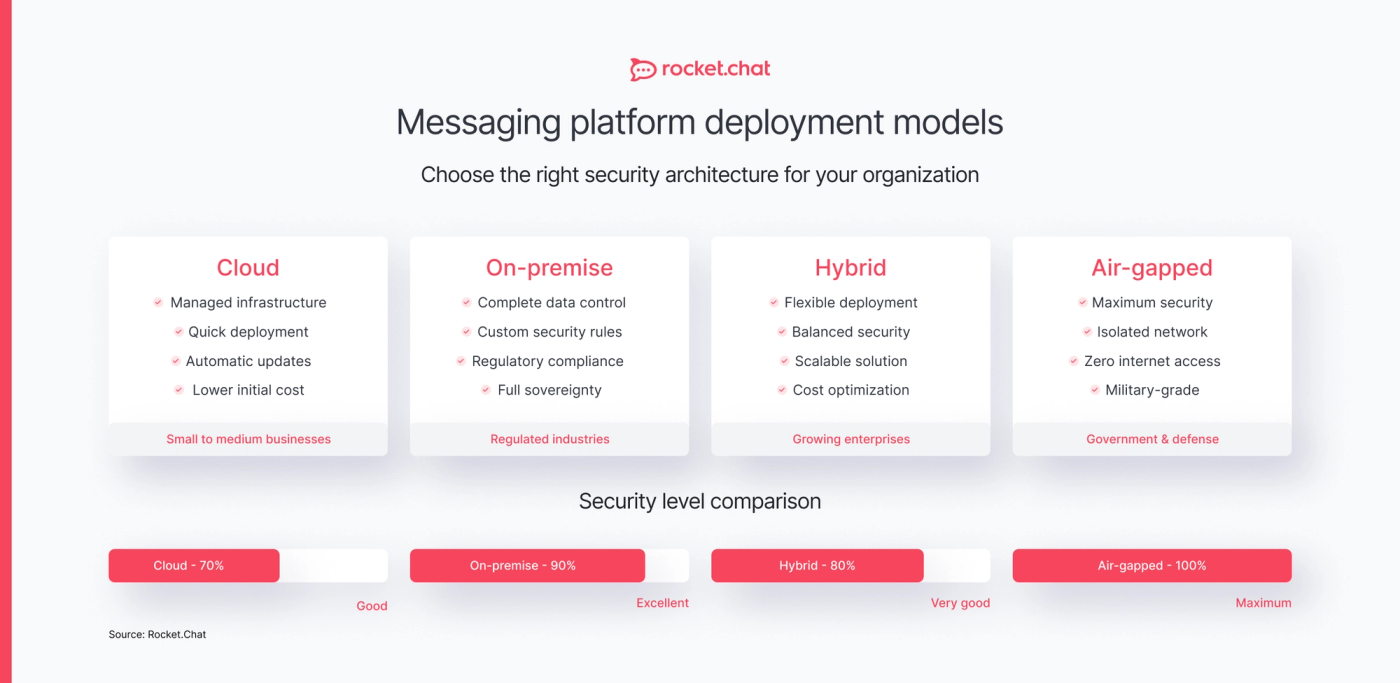
The key is matching the deployment approach to the operational requirement, not treating one as inherently more sovereign than the other. A government ministry handling sensitive policy coordination may be well-served by a sovereign cloud deployment that meets all regulatory requirements. A defence unit conducting classified operations needs physical isolation.
A critical infrastructure operator may need a hybrid: managed sovereign infrastructure for routine government communication, with an isolated deployment available when primary systems are compromised.
What any of these scenarios share is this: data sovereignty and technical sovereignty must hold regardless of the approach chosen. Your data must stay within the jurisdiction you have defined. And you, not the vendor, must always be able to access it. The implications for secure internal communications infrastructure are significant across every sector.
02Why SaaS platforms fail on data sovereignty and technical sovereignty
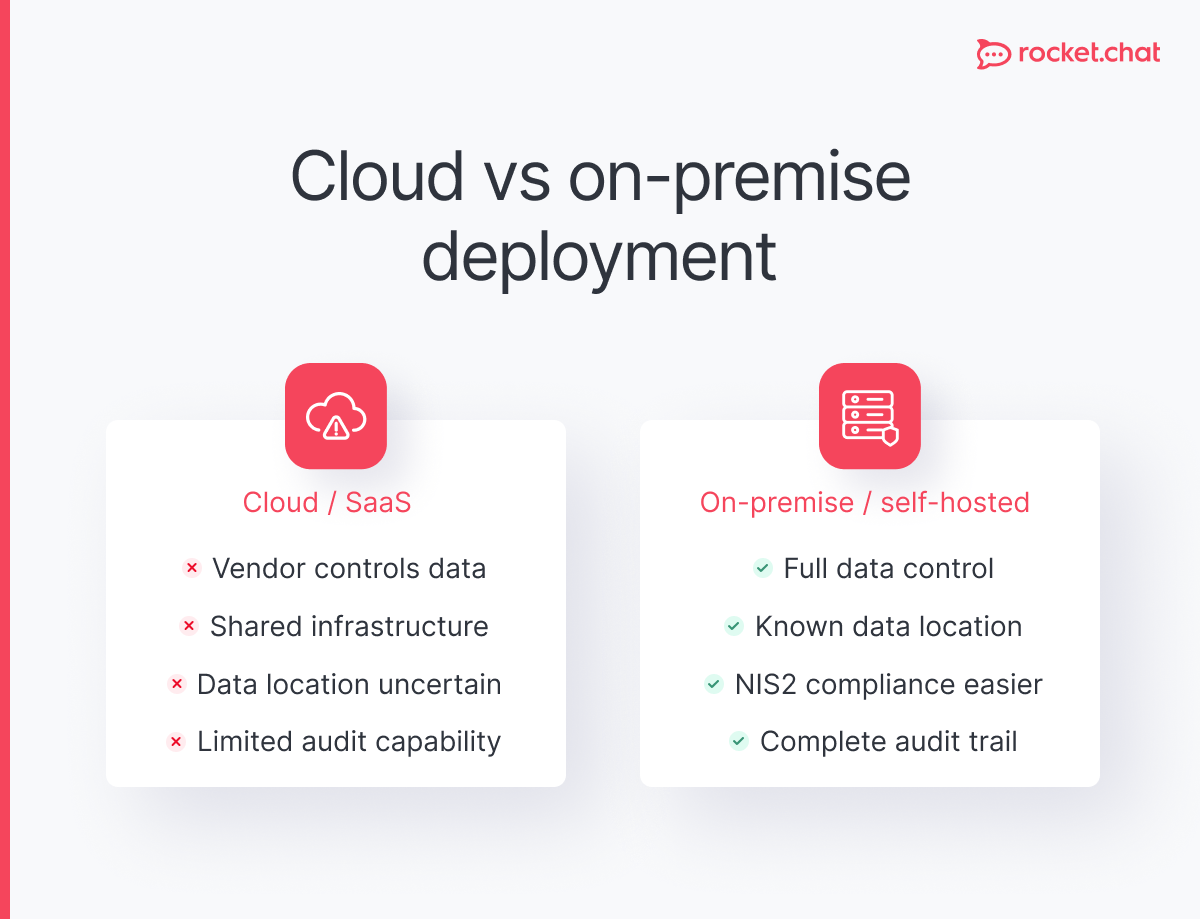
The question is not whether commercial SaaS platforms are secure. Many are well-engineered and invest significantly in their security programmes. The question is whether they deliver data sovereignty and technical sovereignty. By architecture, most cannot.
On data sovereignty: SaaS vendors process your communications in their own infrastructure. Even where they offer EU data centres, the vendor retains administrative access to the underlying systems. The Schrems II ruling from the Court of Justice of the European Union established that this administrative access is the problem. A US company operating an EU data centre still processes European data under US legal jurisdiction. European governments and regulated organisations cannot resolve this through contracts alone.
On technical sovereignty: SaaS platforms manage encryption on the vendor's terms. In most cases, the vendor holds the keys. Customer-managed key options, where they exist, are typically partial; the vendor still controls infrastructure-level access. You cannot move the platform to your own hardware, operate it in a disconnected environment, or guarantee continued access to your communications data if the vendor changes its terms or becomes subject to a foreign government's legal demands.
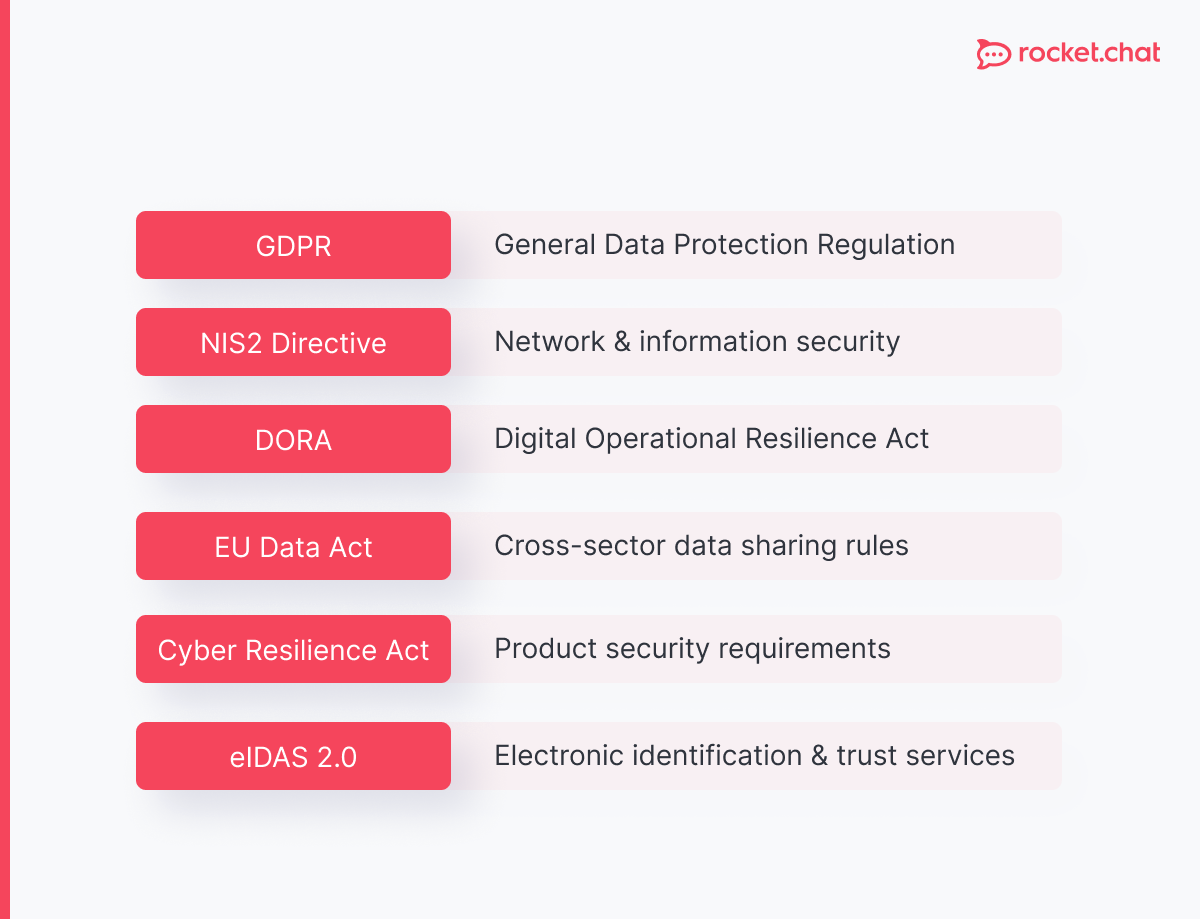
The NIS2 Directive frames this as a supply chain risk. Operators of essential services must formally manage and mitigate vendor dependencies in critical systems. A communications platform where the vendor retains infrastructure access is a dependency that must be addressed, not accepted.
Organisations evaluating Teams alternatives or Slack alternatives for regulated environments are not looking for feature parity. They need a data sovereignty platform where residency and access controls are built into the architecture, not added through contractual clauses. The consequences for secure government messaging are direct: if the vendor can access your communications or be compelled to hand them over, the platform cannot be used for sensitive coordination regardless of how it is configured. That requirement leads to self-hosted deployment: a sovereign communications platform that runs on your infrastructure, under your governance, with no vendor access at any layer.
03Key capabilities for a sovereign communications platform
Not all self-hosted or on-premises tools deliver genuine sovereignty. These are the capabilities that define a sovereign communications platform regardless of which deployment approach you use.
- Data residency controls. The platform must allow you to specify and enforce where data is stored and processed: within EU territory, within a specific member state, or within your own infrastructure. This applies to messages, voice traffic, files, and metadata. Meeting NIS2 compliance obligations requires this to be architectural, not advisory.
- Encryption and access independence. Your organisation must hold the encryption keys. The vendor must have no ability to decrypt your communications and no administrative path that third parties could use to compel access. This is the operational definition of technical sovereignty: you always have access to your data, and access is not contingent on the vendor's continued cooperation.
- Deployment flexibility. A sovereign communications platform must support the full range of deployment models: managed sovereign cloud, private cloud, on-premises, hybrid, and air-gapped. Meeting GDPR requirements is achievable across different deployment approaches, but the platform must support whichever model your operational environment and threat model require.
- Open-source codebase. A platform you cannot inspect is a platform you must trust. Open source allows your security team, auditors, and assessors to verify the security posture directly, a requirement in formal accreditation processes. The European Commission's open-source strategy reflects this: 58% of EU institutions are exploring open-source alternatives specifically for better autonomy and adaptability (European Commission OSPO survey, 2023).
- Comprehensive audit logging. Full audit trails covering who accessed what, when, from where, and what actions they took must be generated and retained within your own environment, under your own policies. This is a baseline requirement for organisations in regulated industries and a formal obligation under most European security frameworks.
- Standards-based federation. Secure government messaging across organisational boundaries requires the ability to communicate with agencies, ministries, or coalition partners without forcing them onto your infrastructure. Federation via Matrix, XMPP, or SIP enables this without creating uncontrolled data residency gaps. For self-hosted communications, governed federation is what separates a sovereign deployment from an isolated one.
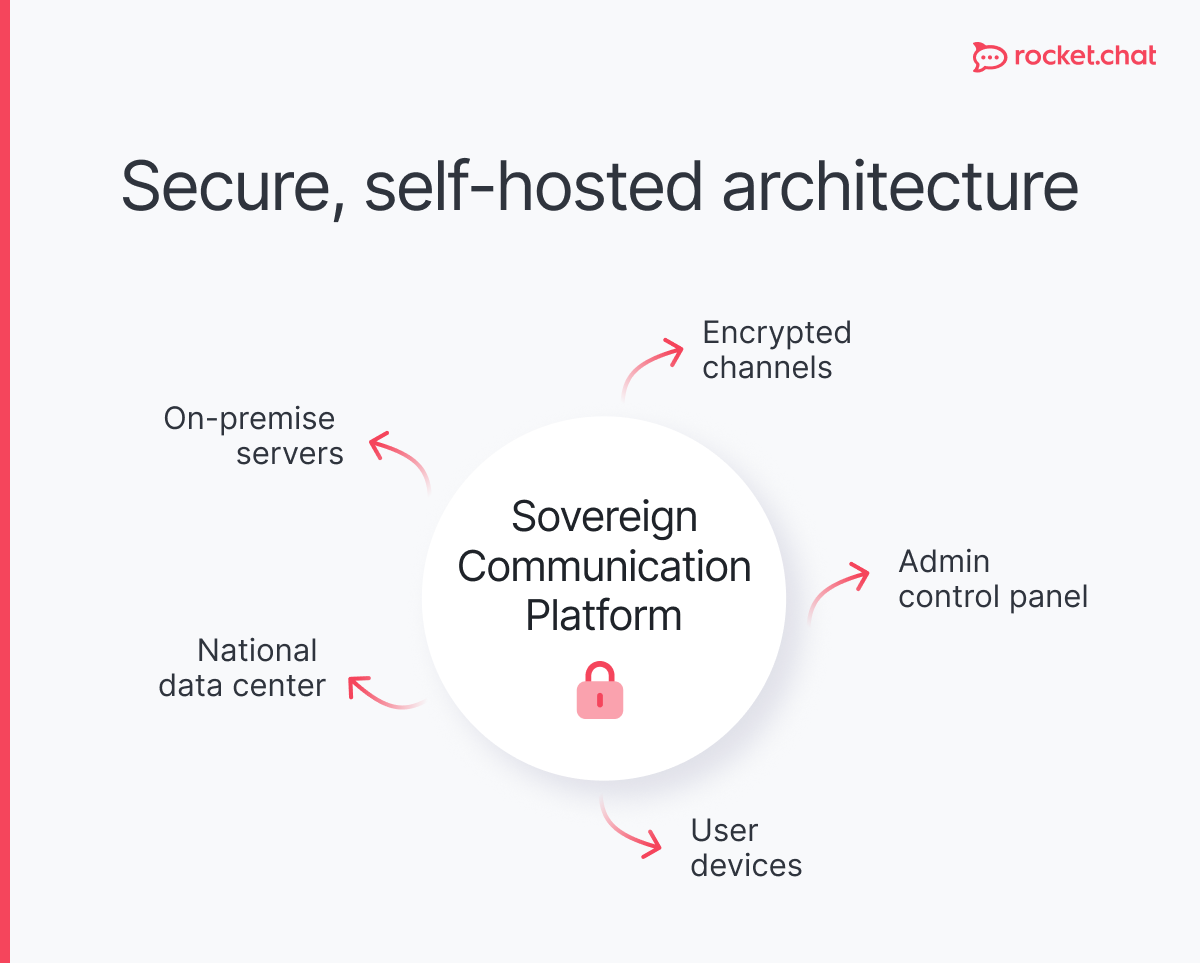
The practical trade-offs between deployment models are covered in depth in the comparison of self-hosted and SaaS communications.
04How to evaluate sovereign communications platforms
The market for sovereign communications platforms has matured into three categories relevant to public sector and regulated enterprise buyers.
1. Open-source platforms with self-hosted deployment
Open-source platforms with self-hosted deployment deliver sovereignty through architecture and transparency. The codebase can be inspected, the deployment is entirely within your control, no vendor dependency exists at the infrastructure layer, and a permissive MIT licence avoids AGPL compliance obligations that create procurement friction at scale. These platforms support the broadest range of deployment models, from managed sovereign cloud to fully air-gapped on-premises.
2. Purpose-built secure messaging platforms
Purpose-built secure messaging platforms are designed for high-assurance environments, sometimes with formal government accreditation. They trade extensibility for specialisation, appropriate where accreditation requirements are the primary constraint.
3. Commercial platforms with self-hosted options
Commercial platforms with self-hosted options offer familiar interfaces and feature breadth but often retain vendor dependencies in authentication infrastructure, licensing, or update mechanisms. These dependencies matter when evaluating technical sovereignty precisely rather than approximately.
For critical infrastructure operators, the evaluation must include resilience under degraded or disconnected conditions. ENISA's Threat Landscape 2024 identifies ransomware, DDoS, and supply chain attacks on essential services as the dominant threat categories. A platform that fails when external connectivity is lost is a liability precisely when secure communications matter most.
For government chat deployments across agencies and departments, federation governance and audit depth take priority. Self-hosted communications must hold up across organisational boundaries without compromising the data residency or access independence that defined the deployment. And for organisations using managed sovereign cloud infrastructure, a data sovereignty platform must still meet the same residency and access-independence tests as a fully on-premises one.
The table below maps the key sovereignty criteria across the three platform categories.
| Capability | Open-source self-hosted | Commercial SaaS | Purpose-built secure platform |
|---|---|---|---|
| Self-hosted deployment | Yes | No | Yes |
| Customer-controlled encryption keys | Yes | Rarely | Yes |
| Air-gapped operation | Yes | No | Yes |
| Open-source codebase | Yes | No | Varies |
| Comprehensive audit logging | Yes | Partial | Yes |
| Standards-based federation | Yes (Matrix/XMPP/SIP) | Limited | Varies |
| Extensibility (APIs, SDKs) | High | High | Low |
| Formal accreditation support | Yes | Limited | Yes |
| Vendor cloud dependency | None | Full | None |
| Permissive licence (MIT) | Yes | N/A | Varies |
Frequently asked questions
What is a sovereign communications platform?
A sovereign communications platform gives an organisation control over where its communications data is stored, who can access it, and how it is protected. Two properties define it: data sovereignty, meaning data is stored and processed within a designated geographic region or jurisdiction, and technical sovereignty, meaning the organisation always has access to its data and no vendor controls it. Where on the deployment spectrum an organisation sits depends on its regulatory context and threat model.
What is the difference between data sovereignty and technical sovereignty in communications?
Data sovereignty means that messages, voice traffic, and files are stored and processed within a designated geographic region or jurisdiction, such as within the EU or within national territory, to satisfy regulatory requirements. Technical sovereignty means your organisation always has access to its communications data and no vendor controls it — the vendor cannot cut off your access by changing its terms, and cannot be compelled by a third party to hand over your data. A platform can offer geographic data residency without technical sovereignty, but not the reverse.
Does hosting data in an EU data centre make a SaaS tool sovereign?
No. The Court of Justice of the European Union's Schrems II ruling established that the physical location of data is not the determining factor. Vendor access is. A US company operating an EU data centre still processes European data under US legal jurisdiction, and can be compelled to provide access to that data regardless of where it is stored. True data sovereignty requires that the organisation, not the vendor, controls the infrastructure and the legal framework governing access to it.
What regulations require sovereign communications in Europe?
GDPR requires organisations to maintain control over personal data processing, including communications. NIS2 requires operators of essential services to manage supply chain security risks, which includes vendor dependencies in communications infrastructure. The Schrems II ruling restricts data transfers to jurisdictions without adequate privacy protections. Taken together, these frameworks create strong regulatory pressure toward self-hosted and sovereign deployment models for European public sector and critical infrastructure organisations.
Does a sovereign communications platform have to be air-gapped?
No. Air-gapped deployment, where the platform operates with no external network connectivity, is one point on the deployment spectrum, appropriate for classified networks, intelligence operations, and certain defence environments. Many organisations achieve meaningful data sovereignty and technical sovereignty through on-premises or sovereign cloud deployment without requiring full network isolation. The key requirement is that air-gapped operation is an available option if the threat model or classification requirements demand it.
Can an open-source communications platform meet enterprise security requirements?
Yes, and in regulated environments, open source often strengthens the security case. An open-source codebase allows security teams, auditors, and third-party assessors to inspect the platform directly rather than relying on vendor attestation — a practical requirement in formal accreditation processes. Independently audited certifications such as SOC 2 Type II and ISO 27001 provide additional third-party validation alongside code transparency.
What is the difference between self-hosted communications and a data sovereignty platform?
Self-hosted communications describes a deployment model in which the organisation runs the software on its own infrastructure. A data sovereignty platform is a broader concept: it requires not just self-hosted deployment but that the organisation retains legal and operational control over where data is processed, who can access it, and how it is encrypted. Not all self-hosted tools qualify if they retain vendor dependencies in key management, authentication, or update infrastructure that undermine technical sovereignty.