Most critical infrastructure organizations are running communications on platforms built for the wrong threat model. Commercial SaaS tools were designed for persistent internet connectivity and vendor-managed infrastructure. Neither holds in energy grids, water systems, transport networks, or healthcare environments facing active cyber threats.
Secure messaging for critical infrastructure is not a feature upgrade. It is an architectural decision. The platform must run under operator control, operate independently of external networks when required, and generate the audit record demanded by compliance frameworks and incident investigation. The gap between what most organizations use today and what those requirements demand is significant.
01Why standard messaging tools fail critical infrastructure operators
The average cost of a data breach in the industrial sector reached $5.56 million in 2024, up 18% from the previous year, according to IBM's breach research. A large share of those costs comes not from the initial intrusion but from delayed detection and fragmented incident response. When the communications platform is a dependency of the compromised infrastructure, coordination breaks down at the worst possible moment.
State-sponsored threat actors understand this dynamic. CISA has documented how China's Volt Typhoon group pre-positioned within communications systems across critical infrastructure sectors, specifically to degrade response capability during future operations. The messaging platform is not a neutral tool in that scenario. It is a target.
The practical failures of commercial SaaS messaging in critical infrastructure environments come down to three points.
1. Data residency: messages, metadata, and user activity are processed on vendor infrastructure with no operator visibility into where or how.
2. Connectivity dependency: the platform fails when primary networks fail, at the exact moment operational communication is most critical.
3. Accreditation: commercial SaaS tools have no pathway to formal authorization in regulated or classified environments.
Critical infrastructure cybersecurity frameworks, including the ENISA threat landscape for EU sectors, consistently identify communications infrastructure as a high-value target. The messaging tool an organization chooses is part of its attack surface.
02What NIS2 compliant messaging actually requires
The NIS2 Directive, which came into force across EU member states in October 2024, establishes binding cybersecurity requirements for essential and important entities across 18 sectors. Its scope covers energy, transport, water, healthcare, digital infrastructure, public administration, and others. The European Commission's implementing regulation, published October 2024, sets specific technical requirements. For a detailed breakdown of how the directive applies to communications platforms, see the overview of NIS2 requirements.
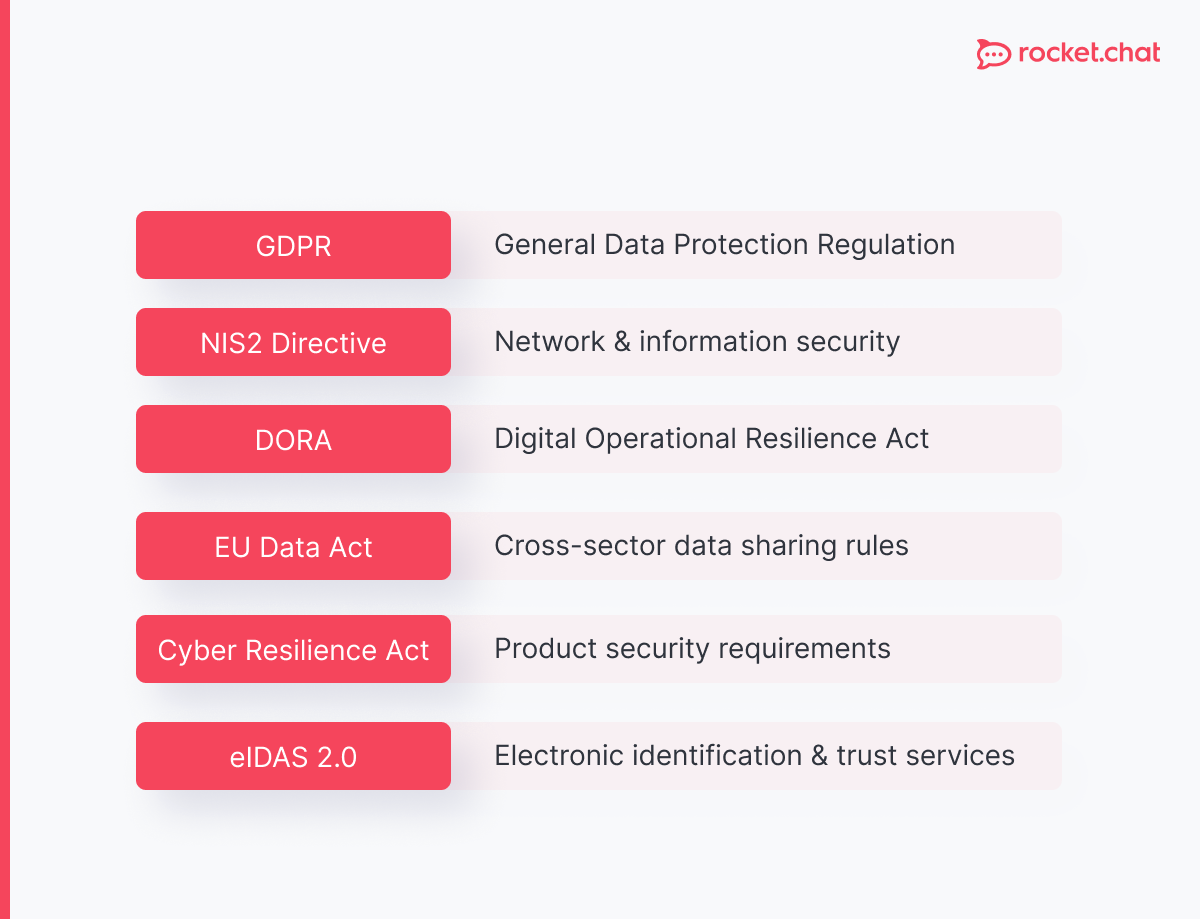
The directive requires "appropriate and proportionate technical, operational and organisational measures" to manage risk to network and information systems. For messaging, the practical translation is:
operators must demonstrate control over where data is stored, who can access it, and what the security posture of the platform is.
For EU operators, GDPR adds a parallel layer of obligation on data processing and residency that intersects directly with NIS2. The combined requirements for messaging are covered in this guide to GDPR compliant messaging.
NIS2 compliant messaging has four non-negotiable characteristics:
- The platform must run on infrastructure the operator controls
- Encryption must be end-to-end, with key management under operator authority — the differences between encryption approaches across platform categories are covered in this overview of messaging encryption standards
- Logging must be comprehensive, covering access events, message activity, and administrative changes
- Data retention must be configurable to match the organization's compliance and legal obligations.
Consumer and commercial SaaS platforms fail at least two of these before the evaluation begins. The approach for regulated environments is substantially different, as covered in this comparison of regulated industries platforms.
03Out-of-band communications: the resilience layer operators miss
Out-of-band communications refers to a channel that operates independently of primary networks and infrastructure. In critical infrastructure cybersecurity, it is the channel an organization uses when primary systems are compromised, overloaded, or unavailable.
Out-of-band communications are not a contingency plan. They are the primary coordination mechanism for incident response. If the messaging platform used during an incident is reachable via the same network the attacker has already penetrated, the response is compromised from the first message.
Effective out-of-band channels share three characteristics:
1. they run on separate infrastructure from primary operational systems,
2. they are capable of operating in disconnected or degraded conditions, and
3. they are already in active use before an incident occurs.
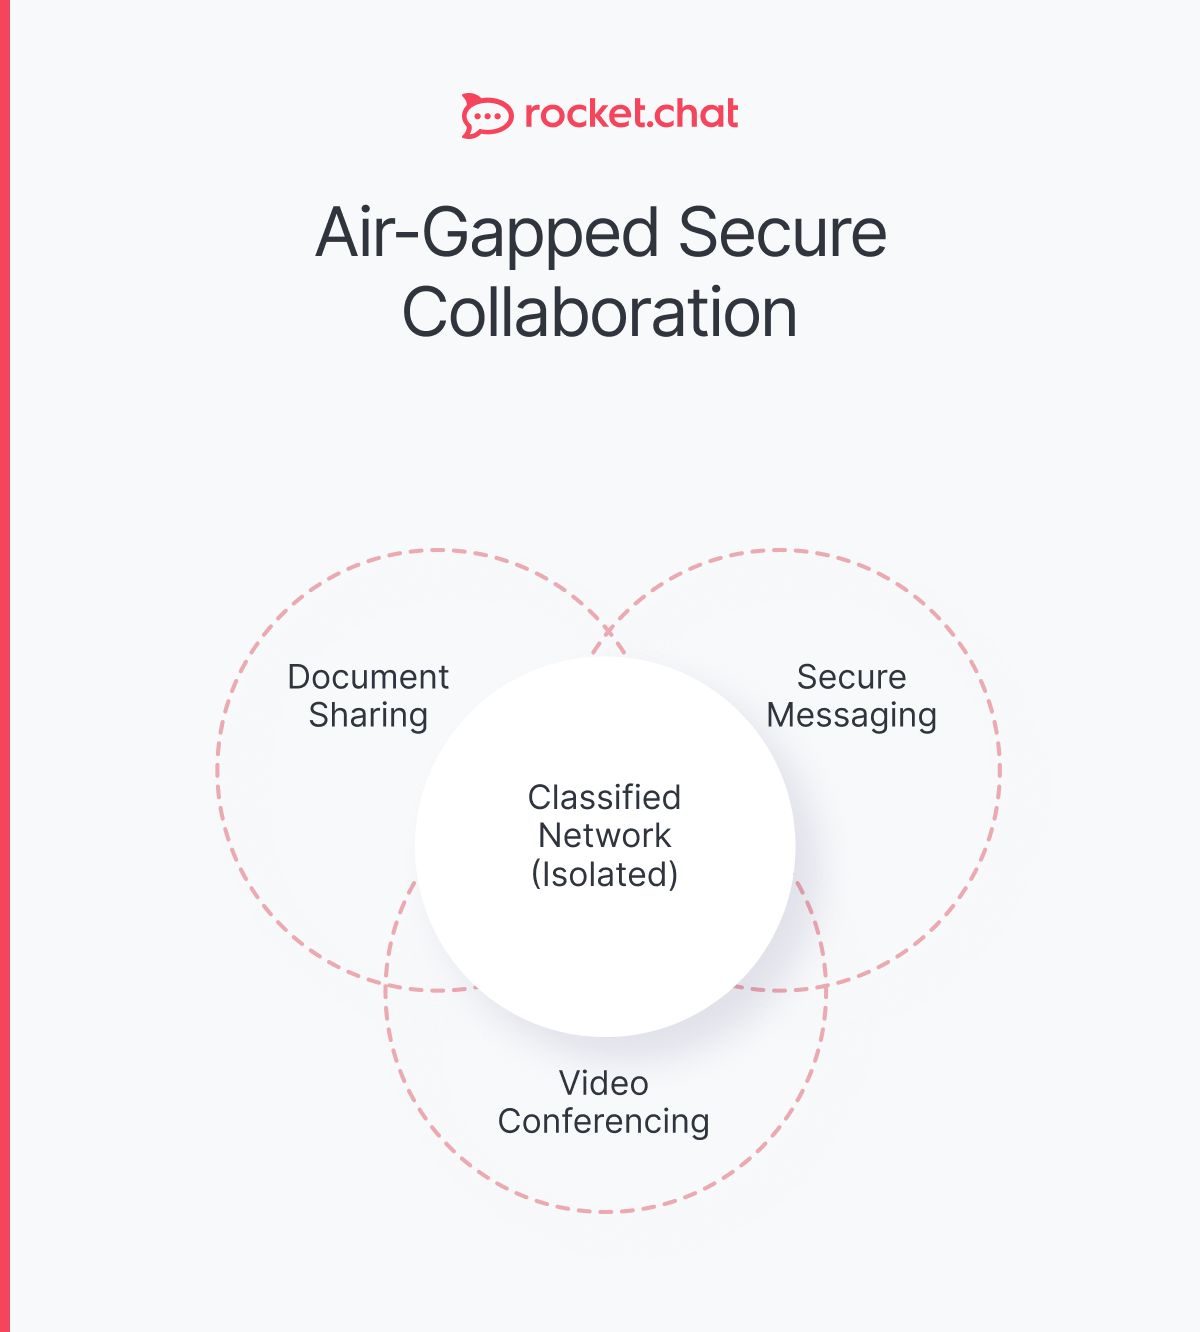
A tool stood up during an active incident is not useful. For organizations that need to understand what this looks like technically, the configuration options for air-gapped deployments are documented in detail. The critical constraint is that out-of-band capability requires a self-hosted platform. SaaS tools cannot serve this function.
04What to look for in a secure messaging platform
The criteria for secure messaging in critical infrastructure environments are specific, and most commercial platforms eliminate themselves quickly against them.
Self-hosted deployment
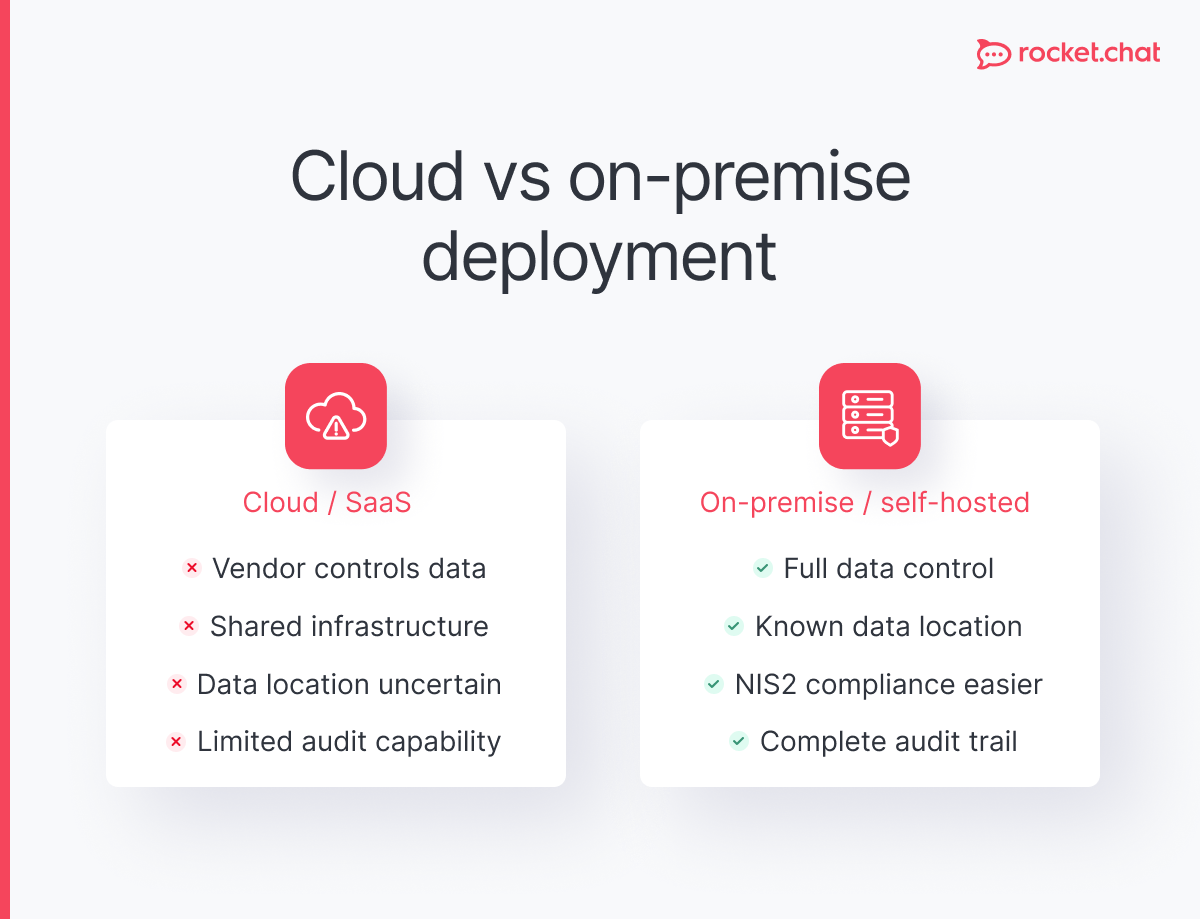
Self-hosted deployment is the baseline, and it means more than choosing where data is stored. A self-hosted platform gives the operator complete control over the deployment environment, the update cycle, the network configuration, and the data path.
That means the organization controls when patches are applied, which networks the platform can reach, and whether any telemetry leaves the environment. It also means that if the vendor ceases to operate or changes its terms, the platform continues running.
For critical infrastructure operators who must maintain communications under any circumstance, vendor dependency is an operational risk. Self-hosted deployment eliminates it. The practical differences between these models are covered in the analysis of self-hosted vs SaaS communications options.
Air-gapped operation
Air-gapped operation extends self-hosting to its logical conclusion for the highest-sensitivity environments. An air-gapped deployment runs on a network with no external internet connectivity — no data in, no data out, unless explicitly authorized through controlled interfaces.
For operators managing operational technology (OT) environments, classified networks, or out-of-band channels, this is not an edge case. It is the operational requirement. A platform that qualifies must be installable from local media, updateable without internet access, and fully functional without any external dependency — including licensing servers, update endpoints, or authentication services that phone home to a vendor.
Most commercial platforms fail on at least one of these points even when deployed on-premises.
Open-source codebase
Open-source codebase is a strategic advantage that has moved from optional to increasingly policy-mandated. In high-assurance environments, security cannot rest on vendor assurances alone. An open-source platform can be audited, inspected, and verified by the operator's own team or a trusted third party, without vendor cooperation.
The European Commission’s Tech Sovereignty Package, published June 2026, places open source explicitly at the center of EU digital policy: the Cloud and AI Development Act requires open-source components in public digital infrastructure, and the package sets a target of 30 million active users of open-source collaboration tools by 2030.
For critical infrastructure operators in EU member states, this is the direction of regulatory travel — open source is increasingly a procurement and policy expectation, not a preference. An MIT-licensed platform specifically avoids the licensing complications that arise with AGPL and similar models, which matters when integrating with complex operational environments.
Extensibility
Extensibility through governed APIs and an application framework allows operators to integrate messaging with existing OT/IT tooling, incident management systems, and operational dashboards. The key word is governed: custom extensions should operate within a controlled, auditable framework, not as unscoped plugins with broad system access.
Federation
Federation enables secure cross-organization communication with agencies, contractors, and partners without requiring all parties to share a single deployment. This is a critical requirement for multi-agency incident response — and it also protects against vendor lock-in by letting different organizations choose different platforms while still communicating across boundaries.
The practical value of this has already been demonstrated at scale. In Sweden, Trafikverket (the Swedish Transport Administration) runs Rocket.Chat, while Försäkringskassan uses a separate Matrix-based system. Despite running entirely different platforms on separate infrastructure, employees of both agencies communicate directly with each other, as documented in this eSam report (in Swedish).
Digital sovereignty is not an abstraction in this context. It is an operational and regulatory requirement. For organizations still working out what that means for their communications stack, this piece on digital sovereignty frames the governance considerations clearly.
05Comparing secure messaging options for critical infrastructure
The table below compares three platform categories against the requirements that matter in critical infrastructure environments.
| Requirement | Rocket.Chat self-hosted | Commercial SaaS Teams, Slack | Consumer encrypted apps Signal, WhatsApp |
|---|---|---|---|
| Self-hosted deployment | Yes | No | No |
| Air-gapped operation | Yes | No | No |
| End-to-end encryption | Yes | Partial | Yes |
| Customer-controlled encryption keys | Yes | No | No |
| Full audit logging | Yes | Partial | No |
| Configurable data retention | Yes | Partial | No |
| NIS2 / regulatory alignment | Yes | Limited | No |
| Formal accreditation path | Yes | No | No |
| Out-of-band capable | Yes | No | Limited |
| Open-source codebase | Yes | No | Partial |
| Federation across organizations | Yes | Partial | No |
| No vendor access to message data | Yes | No | No |
Commercial SaaS platforms occupy a narrow middle ground: feature-rich for standard enterprise use, but architecturally unsuited to the sovereignty, accreditation, and resilience requirements of critical infrastructure. Consumer encrypted apps solve the encryption problem but introduce governance, auditability, and organizational control problems that are just as serious.
Operators who need to run communications under their own control, in their own infrastructure, with an audit trail they own, need a self-hosted platform built for that purpose from the start.
Frequently asked questions
What is secure messaging for critical infrastructure?
Secure messaging for critical infrastructure refers to communications platforms designed to meet the operational, regulatory, and security requirements of sectors such as energy, water, transport, and healthcare. These platforms must support self-hosted deployment, end-to-end encryption with operator-controlled keys, comprehensive audit logging, and the ability to operate in disconnected or degraded network conditions. They differ fundamentally from commercial SaaS tools, which depend on vendor-managed cloud infrastructure and cannot meet formal accreditation requirements.
Why can't critical infrastructure operators use standard SaaS messaging tools?
Commercial SaaS platforms such as Microsoft Teams or Slack store data on vendor-managed infrastructure, have no option for air-gapped or fully isolated deployment, and provide no formal pathway to regulatory authorization or accreditation. For critical infrastructure operators subject to NIS2 or national equivalents, these limitations are not edge cases. They are disqualifying requirements. Any platform that cannot run under the operator's own infrastructure control cannot be the primary communications tool in a regulated or high-assurance environment.
What does NIS2 require for messaging and communications?
NIS2 requires essential and important entities to implement appropriate technical, operational, and organizational measures to manage cybersecurity risk. For messaging platforms, this means: data must be stored and processed on infrastructure the operator controls; encryption must be end-to-end with customer-managed keys; access and message activity must be logged comprehensively; and data retention must be configurable to align with legal and compliance obligations. Operators should consult their own legal and compliance advisors to assess how NIS2 applies to their specific environment and jurisdiction.
What are out-of-band communications and why do critical infrastructure operators need them?
Out-of-band communications refers to a channel that operates independently of primary networks and infrastructure. In critical infrastructure environments, it is the coordination mechanism used when primary systems are unavailable, compromised, or under active attack. An effective out-of-band channel must run on separate infrastructure, be capable of operating without internet connectivity, and be in active use before an incident occurs. Organizations that rely on SaaS tools for this function have no out-of-band capability: if the primary network fails, the tool fails with it.
What is the difference between end-to-end encryption and transport encryption?
Transport encryption (TLS) protects messages in transit between the client and the server, but the service provider can still read message content at rest on their servers. End-to-end encryption ensures that messages are encrypted at the sender's device and can only be decrypted by the intended recipient. For critical infrastructure operators, end-to-end encryption with customer-controlled key management is the relevant standard: it ensures that no third party, including the platform vendor, can access message content. Many commercial platforms offer transport encryption but not true end-to-end encryption with operator-controlled keys.
How does self-hosted messaging support compliance with NIS2 and other frameworks?
Self-hosted deployment means the operator controls where the platform runs, where data is stored, who can access it, and how it is configured. This control is the foundation of compliance with NIS2, GDPR, and national cybersecurity frameworks that impose data residency and sovereignty requirements. It also enables the operator to align the platform with formal accreditation processes, something that is not possible with cloud-hosted-only tools. Self-hosting does not guarantee compliance by itself, but it is a necessary prerequisite for any organization that must demonstrate data sovereignty to regulators, auditors, or oversight bodies.
Can open-source messaging platforms meet enterprise security requirements?
Yes. For critical infrastructure operators, open source is a security advantage, not a limitation. An open-source codebase can be independently audited, inspected, and verified by the operator's own security team or a trusted third party. This is not possible with proprietary platforms, where security assurances depend entirely on the vendor. Open-source platforms also eliminate vendor lock-in, allow operators to adapt the platform to their specific requirements, and make the security posture verifiable rather than assumed. MIT-licensed platforms specifically avoid the licensing complications that can arise with other open-source models.