01Why the deployment model defines your security posture
For organisations operating under GDPR, NIS2, or national security frameworks, the self-hosted vs SaaS communication platforms differences come down to one question:
who controls the infrastructure your sensitive data lives on?
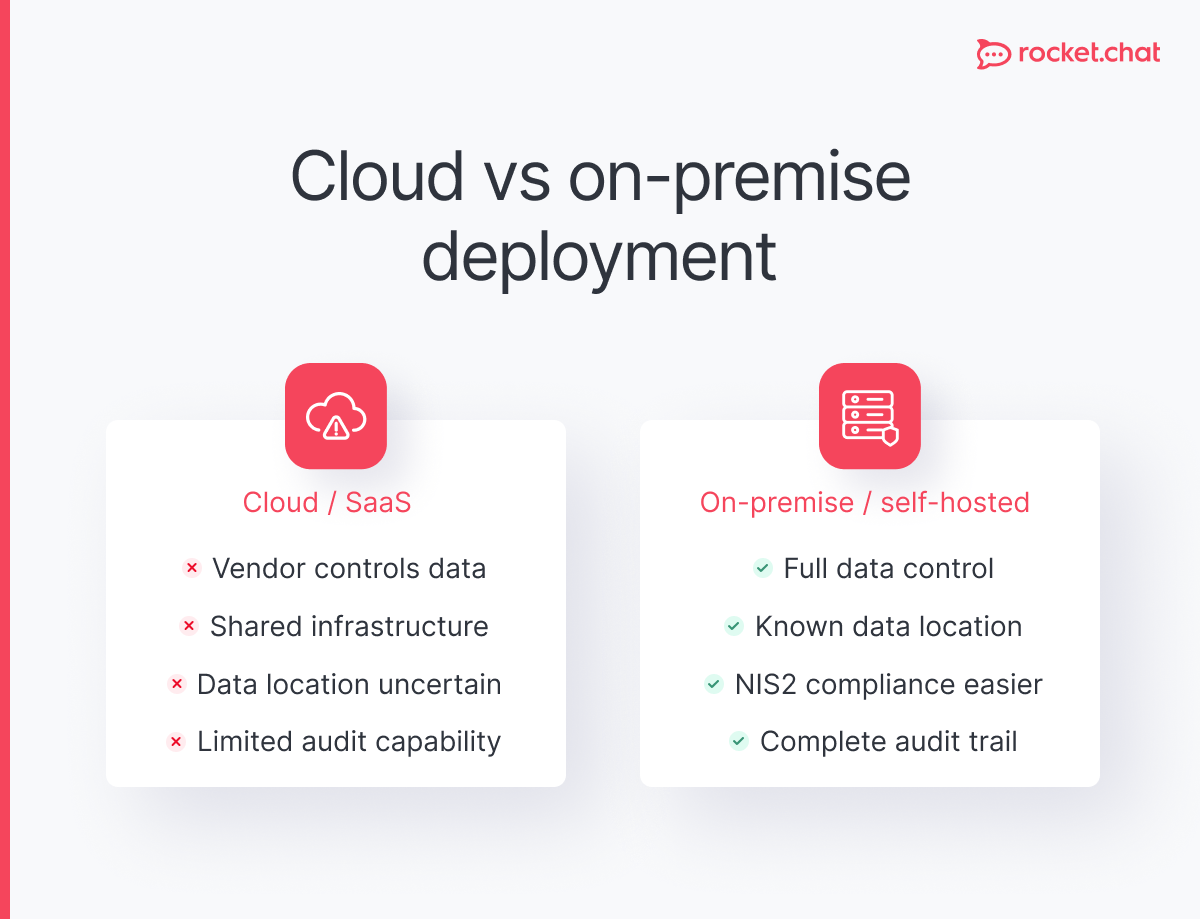
SaaS communication platforms operate on vendor-managed cloud infrastructure. The vendor decides where data is stored, how it is encrypted, and under which legal jurisdiction it falls. For many commercial use cases, this model works. For regulated organisations handling classified, sensitive, or sovereignty-critical communications, it introduces risks that cannot be mitigated through contracts alone.
Self-hosted platforms run inside the organisation's own infrastructure, whether on-premises, in a sovereign cloud, or in an air-gapped environment. The organisation controls encryption keys, access policies, retention rules, and audit logs. No external vendor can access, subpoena, or modify the data without the organisation's knowledge.
This distinction plays out in every procurement decision across regulated sectors. Organisations evaluating secure messaging platforms increasingly treat end-to-end encryption, open-source transparency, and infrastructure ownership as baseline requirements, not differentiators. When the communication channel itself is part of the security perimeter, who controls the infrastructure is not a secondary concern. It is the first question auditors ask.
02The jurisdiction problem SaaS platforms cannot solve
The most consequential difference between self-hosted and SaaS communication platforms is legal jurisdiction.
US-headquartered SaaS providers, even those offering EU-hosted instances, remain subject to the CLOUD Act. This law allows US authorities to compel access to data held by American companies regardless of where that data physically resides. GDPR requires organisations to protect EU citizen data from unauthorised foreign access. The CLOUD Act requires US companies to hand it over. These two obligations are structurally incompatible.
For European government agencies, defence organisations, and critical infrastructure operators, this creates an unresolvable compliance conflict when using SaaS platforms from US vendors. Self-hosted deployment eliminates the jurisdiction problem entirely. The organisation owns the infrastructure, controls the legal environment, and can demonstrate sovereign communication to auditors and oversight bodies.
The European Commission's 2025 Digital Decade report confirmed that a substantial portion of governmental digital infrastructure still depends on service providers outside the EU, a dependency that member states are now actively working to reduce.
03How self-hosted and SaaS platforms compare across critical requirements
The differences between self-hosted and SaaS communication platforms extend beyond hosting location. They affect every layer of the security and compliance stack.
- Data residency and sovereignty. SaaS platforms typically offer region selection, but the vendor retains administrative access and the data remains under their legal control. Self-hosted platforms give the organisation full custody. For sectors where sovereign communication is a regulatory requirement, this is the deciding factor.
- Compliance and accreditation. Achieving NIS2 compliance, NIST 800-53 alignment, or a national security accreditation requires demonstrable control over the communication environment. SaaS platforms provide shared responsibility models where the vendor handles parts of the stack. Self-hosted platforms put the full stack under the organisation's authority, making formal accreditation achievable on the organisation's own terms. The NIS2 directive requires organisations in 18 sectors to implement rigorous cybersecurity measures, with enforcement audits due by mid-2026.
- Operational resilience. SaaS platforms depend on vendor uptime and internet connectivity. In disconnected, degraded, or contested environments, this dependency becomes a liability. Self-hosted platforms can operate on isolated networks, in air-gapped configurations, or during outages and incidents. For defence and emergency response scenarios, this resilience is not optional.
- Customisation and integration. SaaS platforms offer standardised configurations. Self-hosted platforms can be adapted to specific operational workflows through APIs, extensions, and custom integrations. Organisations running unique communication workflows benefit from the ability to build and govern capabilities within the platform rather than working around vendor limitations.
| Capability | Self-hosted platforms | SaaS platforms |
|---|---|---|
| Data residency | Organisation controls physical and legal location | Vendor selects regions; data under vendor's legal jurisdiction |
| Encryption key management | Organisation owns and manages all keys | Vendor manages keys; limited customer control |
| Compliance accreditation | Organisation conducts own accreditation against full stack | Shared responsibility; vendor controls parts of the stack |
| Air-gapped deployment | Fully supported | Not available |
| Operational resilience (DDIL) | Operates without external connectivity | Requires internet and vendor infrastructure |
| Customisation | Full access via APIs, SDKs, and extension frameworks | Limited to vendor-provided configuration options |
| Jurisdictional independence | No foreign legal exposure | Subject to vendor's home jurisdiction laws |
| Audit and logging | Full control over retention, format, and access | Vendor-defined logging; limited export options |
| Update and patch control | Organisation controls timing and scope | Vendor pushes updates on their schedule |
| Total cost of ownership at scale | Lower per-user cost at scale; infrastructure investment required | Predictable per-user pricing; scales linearly with headcount |
04What NIS2 and GDPR mean for platform selection
Regulatory pressure is accelerating the shift toward self-hosted deployment models across Europe.
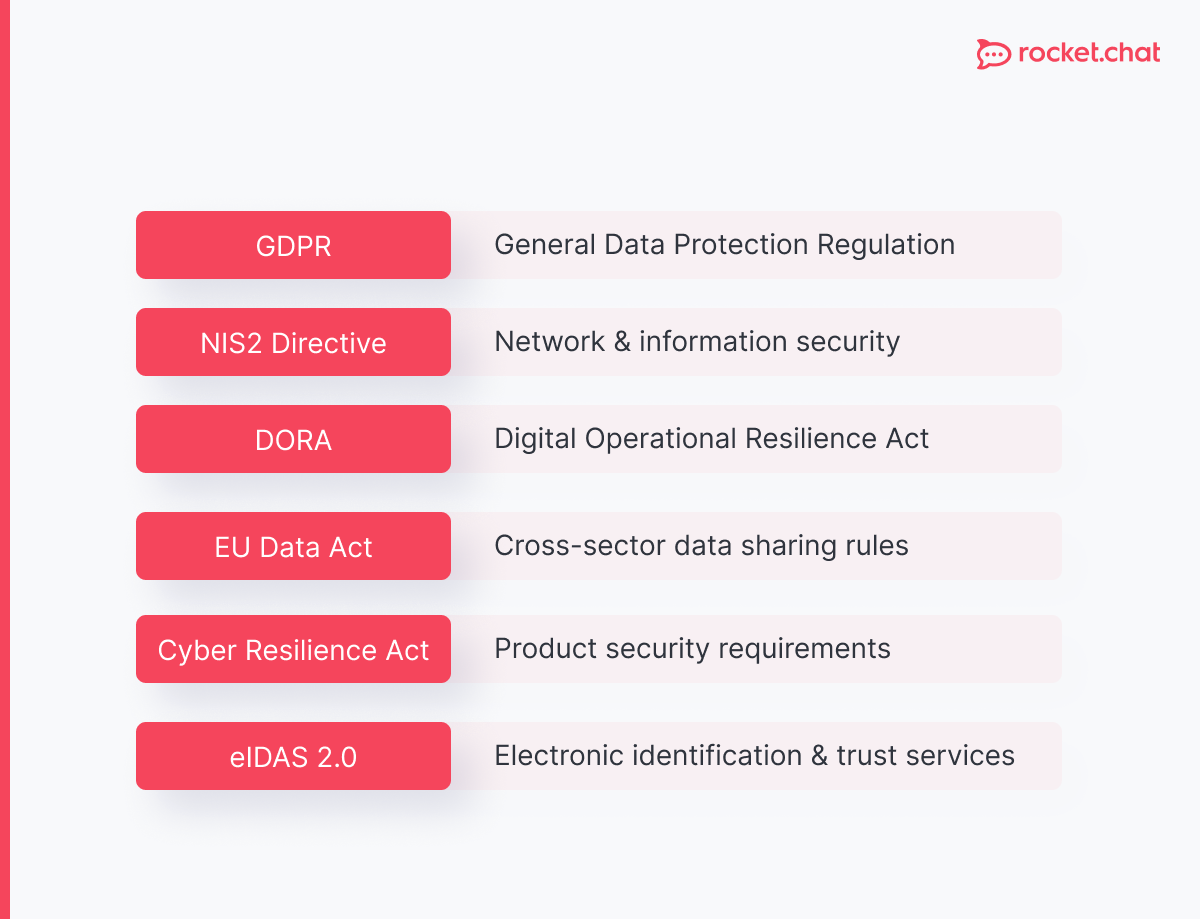
NIS2, which applies to essential and important entities across 18 sectors, requires organisations to implement cybersecurity risk management, incident reporting within 24 hours, and supply chain security assessments. Penalties for non-compliance can reach 10 million euros or 2% of global turnover for essential entities. (Source: ENISA) Senior management is personally liable for failures in cybersecurity governance.
GDPR mandates that organisations demonstrate control over personal data processing, including secure communication channels. When a SaaS provider subject to the CLOUD Act processes EU personal data, the organisation's ability to guarantee GDPR compliance is structurally compromised.
For organisations evaluating chat platforms, the compliance question is straightforward: does the platform enable the organisation to achieve and maintain accreditation independently, or does it create dependencies that auditors will flag?
05Why European organisations are choosing self-hosted platforms
The trend is clear: European spending on sovereign cloud infrastructure will grow from $6.9 billion in 2025 to $12.6 billion in 2026, and is expected to reach $23.1 billion by 2027, surpassing North America. (Source: Gartner, via The Register) Government agencies are the primary buyers.
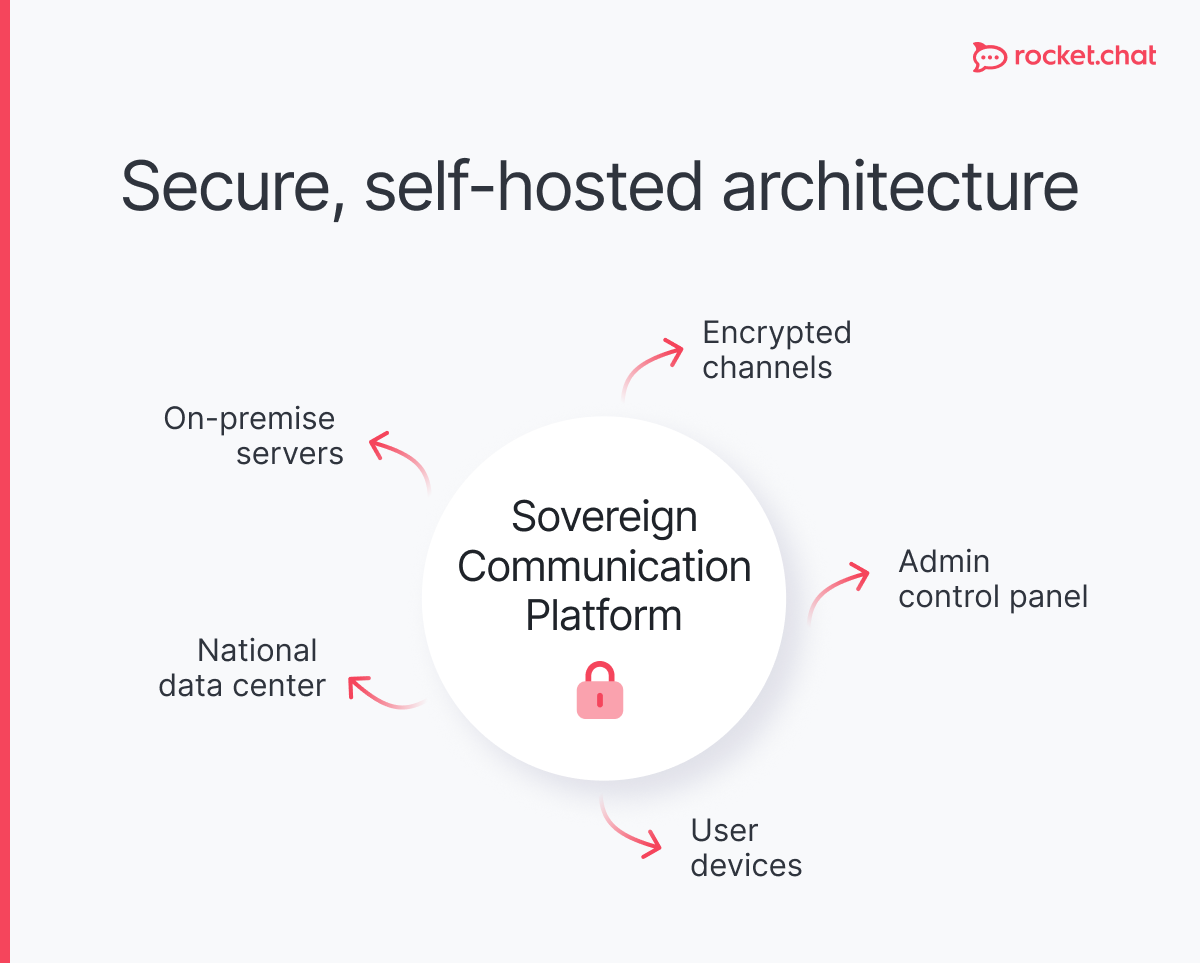
This shift is not driven by preference. It is driven by operational necessity. Organisations that handle classified information, operate in contested environments, or must comply with national security frameworks need communication platforms that operate under their full control. SaaS models, by design, cannot provide this.
Rocket.Chat is built for these requirements. As an open-source, self-hosted secure communication platform, it gives organisations full control over data, infrastructure, and security posture. Deployed across government, defence, and critical infrastructure environments globally, Rocket.Chat supports air-gapped networks, formal accreditation processes, and sovereign collaboration across agencies and allies.
Regulatory and compliance requirements vary by jurisdiction. Organisations should consult their own legal and compliance advisors to determine the specific obligations applicable to their operations.
Frequently asked questions
What is the main difference between self-hosted and SaaS communication platforms?
The primary difference is infrastructure control. Self-hosted communication platforms run on the organisation's own servers or sovereign cloud, giving full custody over data, encryption keys, and access policies. SaaS platforms run on vendor-managed infrastructure, where the vendor retains administrative access and the data falls under the vendor's legal jurisdiction.
Are SaaS communication platforms compliant with GDPR?
SaaS platforms can support GDPR compliance, but providers headquartered outside the EU may be subject to conflicting legal obligations. US-based providers, for example, must comply with the CLOUD Act, which can require them to disclose data to US authorities regardless of where it is stored. This creates a structural tension with GDPR's data protection requirements that organisations should evaluate carefully.
Why are European organisations moving to self-hosted communication platforms?
European public sector and defence organisations are shifting to self-hosted platforms to meet sovereignty requirements, achieve formal security accreditation, and eliminate dependency on foreign-controlled infrastructure. Gartner projects European sovereign cloud spending will grow 83% in 2026, reaching $12.6 billion, with government agencies as the primary buyers.
Can self-hosted platforms work in air-gapped or disconnected environments?
Yes. Self-hosted communication platforms can be deployed on fully air-gapped networks with no internet connection. This makes them suitable for classified environments, defence operations, and critical infrastructure where connectivity cannot be guaranteed. SaaS platforms, by contrast, require continuous internet access and vendor infrastructure availability.
How does NIS2 affect communication platform selection?
NIS2 requires essential and important entities across 18 sectors to implement cybersecurity risk management, rapid incident reporting, and supply chain security assessments. Communication platforms that process sensitive organisational data fall within scope. Self-hosted platforms give organisations direct control over the security measures NIS2 requires, while SaaS platforms introduce shared responsibility models that can complicate accreditation.
Is self-hosted communication more expensive than SaaS?
Self-hosted deployment requires upfront infrastructure investment and internal administration resources. However, at scale, the per-user cost is typically lower than SaaS subscription pricing, which scales linearly with headcount. For large organisations or those with long-term deployment horizons, self-hosted platforms often deliver lower total cost of ownership.
What should regulated organisations look for in a self-hosted communication platform?
Regulated organisations should evaluate self-hosted platforms on five criteria: end-to-end encryption with organisation-managed keys, support for air-gapped and sovereign cloud deployment, open-source code that enables independent security audits, compliance alignment with frameworks like NIS2 and GDPR, and extensibility through APIs and SDKs to support unique operational workflows.