All users are advised to upgrade Rocket.Chat Server to 0.57.4, 0.58.4, 0.59.0 or greater.Rocket.Chat Server version 0.58.3, 0.57.3 and prior versions are vulnerable to a NoSQL injection which can lead to an administrator account takeover.Thank you to Steeve Barbeau for identifying and reporting the vulnerability. The details of the vulnerability will be shared in a future update.If you have any questions, concerns or require advice please contact security@rocket.chat or chat to us on https://open.rocket.chat/channel/support.Nick van den Berg
← All posts
Security Vulnerability in 0.57.3, 0.58.3 and below
Keep reading
Related posts.
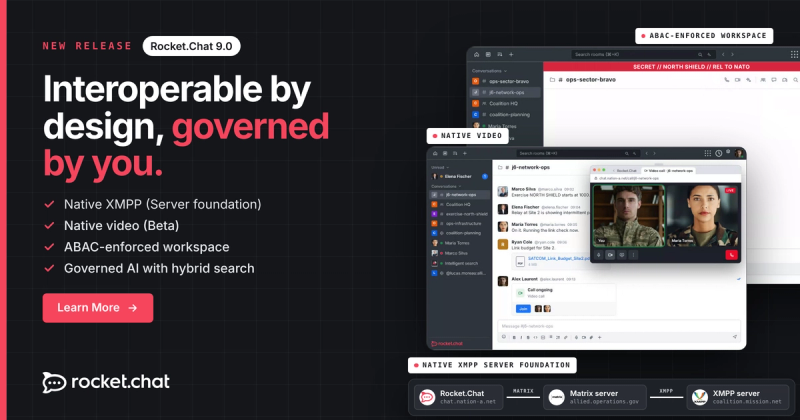 Rocket.Chat 9.0: Interoperable by design, governed by youRocket.Chat 9.0 makes interoperable by design real: a native XMPP server foundation alongside native Matrix, so you and your partners can connect whatever protocol each side runs, without giving up governance or control. Native video completes the real-time comms bundle, and the ABAC-enforced workspace puts every channel inside the access boundary.Read article →9 min read
 Rocket.Chat 8.8 introduces native MCP server for AI agentsConnect any MCP-compatible AI agent to your workspace without custom code, plus private channels encrypted by default.Read article →5 min read
 Rocket.Chat 8.7 brings XMPP interoperability for coalition operationsFederate with XMPP coalition partners on FMN networks from the same platform your teams use every day.Read article →5 min read