Secure messaging for European governments is no longer a niche IT concern. It is a core requirement for operational continuity, legal compliance, and national security. The question for senior decision-makers is not whether to act, but which architecture can meet the full stack of regulatory and threat requirements simultaneously.
The short answer: a government-grade messaging platform must be self-hostable, end-to-end encrypted, auditable, and built on an open-source codebase that can be independently verified. Platforms that fail on any of these criteria expose institutions to data sovereignty violations, NIS2 non-compliance, and adversarial interception risk.
01Why commercial messaging platforms fail the public sector
Most enterprise messaging tools, including those widely adopted in the private sector, were built for global commercial deployment. They store metadata and often message content on infrastructure governed by non-EU law, including the US Cloud Act, which can compel disclosure of data held by US-headquartered providers regardless of where servers are physically located.
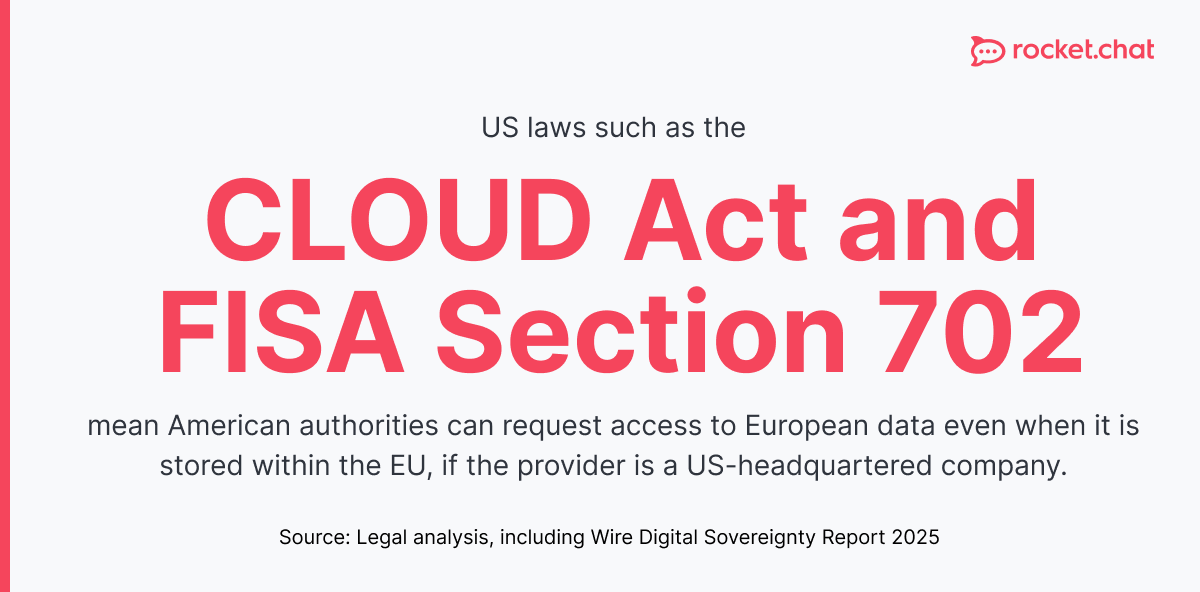
The European Data Protection Board has confirmed that transfers of personal data to US-based processors remain legally precarious, even following the EU-US Data Privacy Framework. For governments handling classified communications, citizen data, or inter-agency coordination, this is an unacceptable legal exposure.
Beyond legality, there is the operational risk. A government chat platform that routes messages through third-party cloud infrastructure introduces interception vectors that on-premise solutions eliminate by design. Signal intelligence agencies of adversarial states actively target government communication channels, and cloud-hosted platforms with opaque infrastructure are significantly harder to audit.
Explore the risk landscape for government communication to understand how threat models differ from the private sector.
02What GDPR compliance actually requires for government messaging
GDPR compliance in a messaging context means more than encryption in transit. It requires documented data processing agreements, clear data retention and deletion policies, the ability to respond to subject access requests, and demonstrable control over where data is stored and who can access it.
Article 28 of GDPR requires that any data processor acting on behalf of a public authority operates under a binding contract that specifies the subject matter, duration, nature, and purpose of processing. Most commercial messaging vendors offer standard data processing agreements that were not designed with government classification requirements in mind.
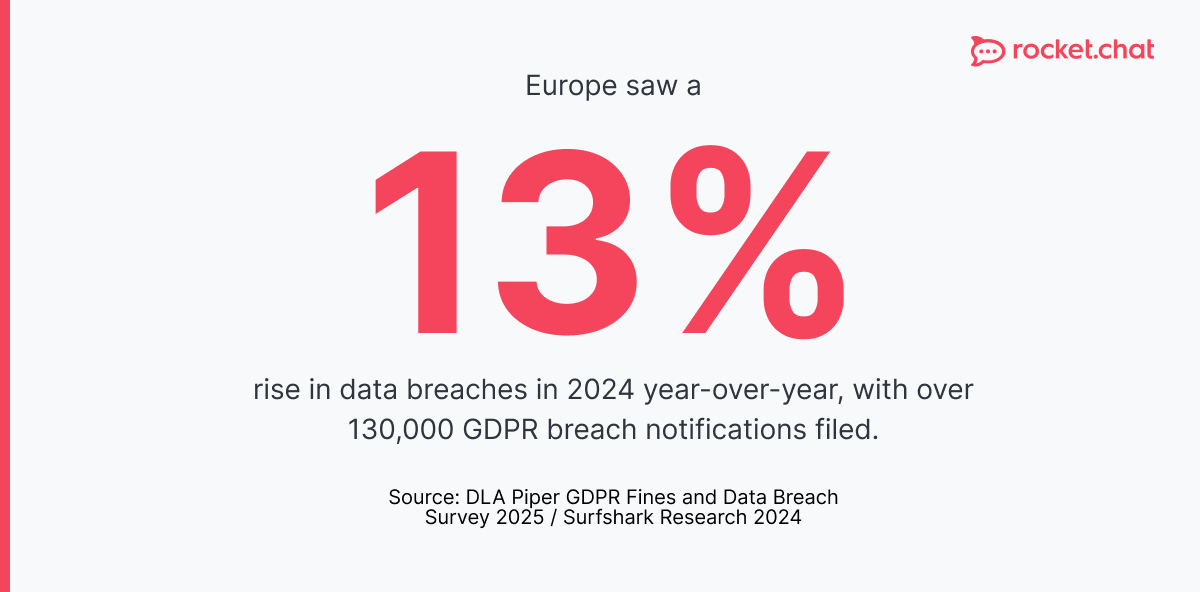
For inter-agency communication, the bar is higher. Governments must demonstrate that GDPR-compliant messaging infrastructure can produce audit logs, enforce retention limits automatically, and restrict access based on security clearance. These requirements rule out most consumer-grade or SME-focused tools.
NIS2 adds a further layer. Entities classified as essential or important under the directive, which includes central government bodies, must implement appropriate technical and organisational measures for network and information security. According to the European Union Agency for Cybersecurity (ENISA), many public sector organisations remain underprepared. Review NIS2 compliance requirements for a detailed breakdown of obligations relevant to communication systems.
03The architecture of secure government messaging
A compliant and operationally resilient messaging platform for government use requires six architectural properties.
- End-to-end encryption ensures that message content is decipherable only by the sender and intended recipient. No intermediary, including the platform vendor, can access plaintext.
- Self-hosting capability allows governments to deploy the platform on infrastructure they control, within their own data centres or on national cloud infrastructure. This eliminates third-party data access risk entirely.
- Air-gap support is required for high-security environments where network isolation is mandatory. Air-gapped collaboration is a practical requirement for defence, intelligence coordination, and critical infrastructure protection.
- Open-source codebase allows independent security audits. Governments cannot verify the security of proprietary black-box systems. Open source is the only architecture that permits genuine auditability.
- Role-based access control (RBAC) enables administrators to enforce least-privilege access, ensuring that users access only the channels and data their role requires.
- Federated identity integration allows platforms to connect with existing government identity providers (LDAP, Active Directory, SAML), reducing the attack surface of standalone credential management.
The most secure messaging apps analysis covers how these properties stack against one another in practice.
04Digital sovereignty as a procurement requirement
Digital sovereignty has moved from political rhetoric to enforceable procurement policy across the EU. Germany's BSI (Federal Office for Information Security) requires that critical government systems use certified products or undergo independent security evaluation. France's ANSSI operates a similar qualification framework. The Dutch government has published explicit guidance against the use of US-headquartered SaaS platforms for sensitive communications.
The common thread is infrastructure control. Digital sovereignty for governments means the ability to operate, audit, and if necessary, modify the communication systems they depend on, without requiring permission or cooperation from a foreign commercial vendor.
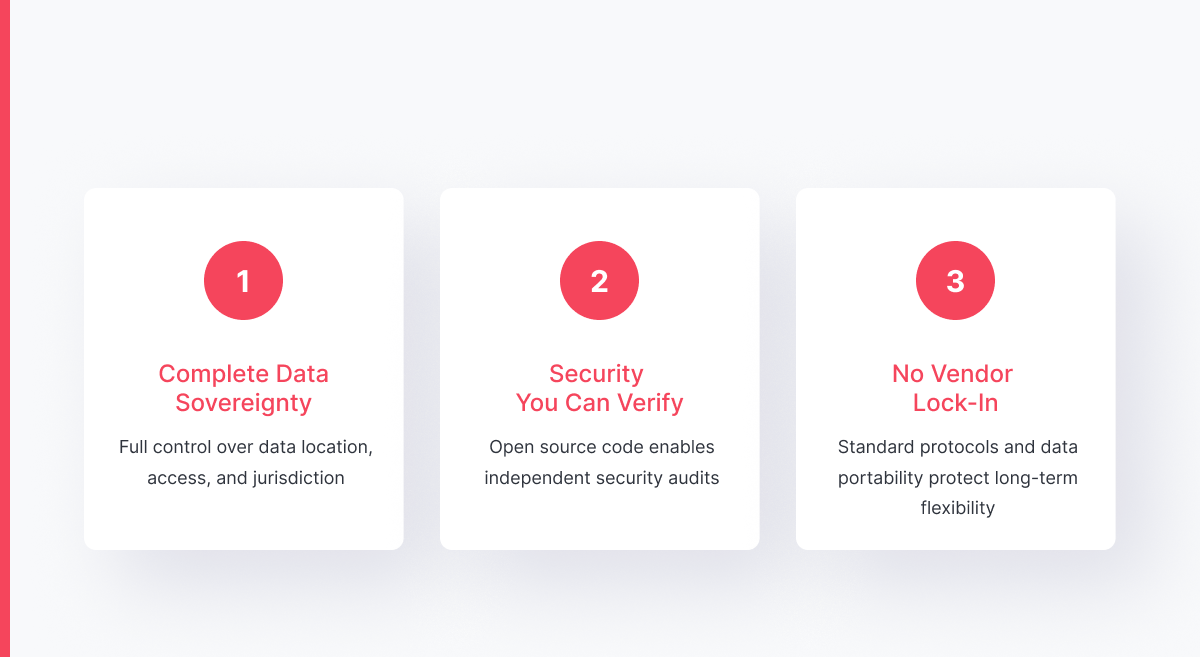
This has direct procurement implications. A platform evaluated as a sovereign Slack alternative for Europe must satisfy not just feature requirements but legal architecture requirements: EU data residency by default, no telemetry to vendor infrastructure, and contractual guarantees that vendor access to government data is technically impossible.
For a structured comparison with widely used commercial tools, the Microsoft Teams alternatives for European government analysis is directly relevant for procurement teams.
05Comparing secure messaging options for European governments
| Capability | Open-source self-hosted | EU commercial SaaS | US commercial SaaS |
|---|---|---|---|
| Data residency control | Full | Partial (contractual) | Limited |
| End-to-end encryption | Yes (configurable) | Varies | Varies |
| Air-gap deployment | Yes | No | No |
| Open-source auditability | Yes | Rarely | Rarely |
| NIS2 alignment | High | Medium | Low |
| GDPR Article 28 compliance | Straightforward | Contractual dependency | Complex |
| Vendor lock-in risk | Low | Medium | High |
| Federation with gov identity providers | Yes | Often | Often |
The table reflects the structural advantages of open-source communication for government. Commercial SaaS options, including those headquartered in the EU, introduce contractual and technical dependencies that self-hosted open-source platforms avoid by design.
06Threat model: what secure messaging must defend against
Government communication systems face a threat model that differs substantially from enterprise deployments. The primary threats are state-level adversaries with signals intelligence capability, insider threats with elevated access, and supply chain compromise of vendor infrastructure.
State-level adversaries do not rely on exploiting individual endpoints. They target infrastructure: transit encryption, metadata, and vendor access pathways. A platform hosted by a US or non-EU cloud provider is subject to legal compulsion that a self-hosted on-premise deployment is not.
Insider threats require technical controls, not just policy. Organisational security frameworks for government should mandate message-level audit logs, access reviews tied to RBAC roles, and the ability to retroactively reconstruct communication timelines for forensic purposes.
Supply chain risk is addressed by open-source architecture and independent code audits. According to the ENISA Threat Landscape 2024, public administration was the most targeted sector across all analysed incidents, accounting for 19% of attacks, with supply chain attacks identified as one of the seven prime threat categories showing continued growth.
Encrypted messaging app selection for government contexts must factor all three threat vectors into the evaluation criteria.
07Shortlist: secure messaging platforms for European governments
Three platforms consistently meet the core architectural requirements for government deployment: self-hosting, end-to-end encryption, open-source auditability, and compatibility with EU data residency obligations.
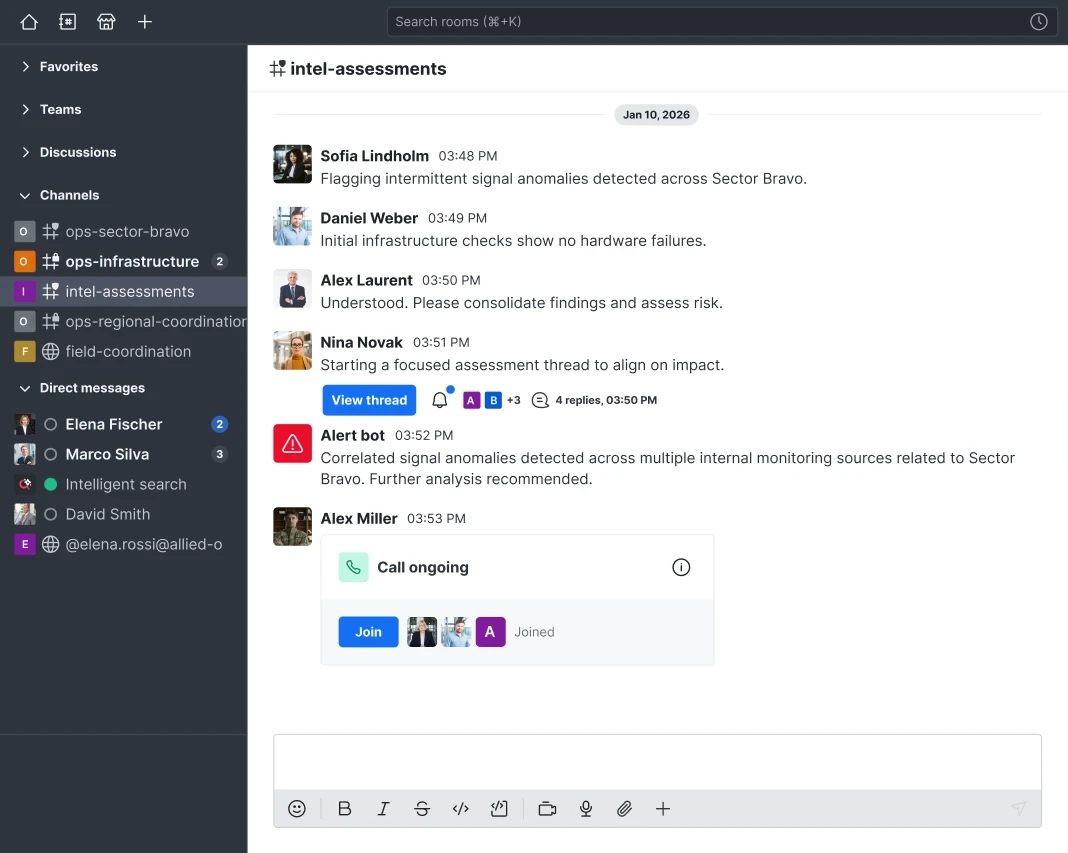
Rocket.Chat is an open-source platform with full self-hosting support, air-gap deployment capability, and federated identity integration via LDAP, SAML, and OAuth. It supports E2EE, role-based access control, and on-premise deployment with no mandatory vendor connectivity. Its architecture is designed to give organisations complete infrastructure ownership, with no telemetry or dependency on vendor-side services. It supports federated messaging across organisational boundaries, allowing inter-agency communication without routing data through external infrastructure. It has been adopted by public sector organisations across Europe and offers a fully auditable codebase.
Element (Matrix) is built on the open Matrix protocol, which provides decentralised, federated messaging with E2EE by default. It supports self-hosted deployment via the Synapse server and is used by several European government bodies, including the German and French public sectors. The federated architecture allows inter-agency communication without routing data through a central vendor.
Wire for Government is a Swiss-headquartered platform offering E2EE, self-hosted deployment, and a dedicated government product tier. It holds BSI approval in Germany and is designed for high-security environments. The codebase is open source and has undergone independent security audits.
All three platforms satisfy the six architectural properties outlined above. For organisations prioritising the broadest deployment flexibility, including air-gap environments and deep identity integration, Rocket.Chat covers the widest range of government use cases out of the box.
Frequently asked questions
What makes a messaging platform compliant with secure messaging requirements for European governments?
A compliant platform must satisfy data residency requirements under GDPR, support deployment on government-controlled infrastructure, provide end-to-end encryption with no vendor access to plaintext, and maintain audit logs sufficient for NIS2 accountability requirements. Platforms hosted on non-EU cloud infrastructure controlled by US-headquartered vendors carry inherent legal risk under the Cloud Act, regardless of where physical servers are located. Compliance is architectural, not just contractual.
Is end-to-end encryption sufficient for government-grade secure messaging?
End-to-end encryption is necessary but not sufficient. It protects message content in transit and at rest, but does not address metadata exposure, infrastructure access by the hosting vendor, or the absence of audit capability. A government messaging system must also support self-hosting, role-based access control, and forensic-grade logging to meet the full scope of NIS2 and GDPR obligations. Encryption without infrastructure control leaves governments exposed to legal compulsion and supply chain risk.
How does NIS2 affect government messaging platform requirements?
NIS2 classifies central government bodies as essential entities, imposing mandatory requirements for risk management, incident reporting, and supply chain security. For messaging platforms, this means that providers must be subject to appropriate contractual controls, that the platform must support rapid incident response and forensic audit, and that supply chain dependencies, including the platform vendor itself, must be assessed for security risk. Platforms that cannot support independent security audits or that process data on opaque third-party infrastructure are structurally difficult to align with NIS2.
What is digital sovereignty in the context of government communication?
Digital sovereignty means that a government retains full operational, legal, and technical control over its communication infrastructure. In practice, this requires that messaging platforms can be deployed on government-owned or government-contracted infrastructure within EU jurisdiction, that no vendor has technical access to message content or metadata, and that the platform can continue operating without dependency on the vendor's commercial continuity. Open-source, self-hostable platforms are the primary architecture that satisfies all three conditions.
Can European governments use US-headquartered messaging platforms for sensitive communications?
The legal risk is significant. US-headquartered providers are subject to the Cloud Act, which allows US law enforcement and intelligence agencies to compel disclosure of data held by those providers, including data stored in EU data centres. The EU-US Data Privacy Framework provides some protections for commercial data transfers but does not neutralise Cloud Act obligations. For communications involving classified material, critical infrastructure coordination, or citizen data, most EU national cybersecurity frameworks advise against or explicitly prohibit the use of such platforms.
What role does open-source software play in secure government messaging?
Open-source platforms allow governments and independent security researchers to audit the full codebase for vulnerabilities, backdoors, and data handling practices. Proprietary platforms cannot provide this assurance. For government procurement, open-source auditability is increasingly treated as a prerequisite rather than a preference, particularly in Germany, France, and the Netherlands, where national cybersecurity agencies have published guidance favouring verifiable, auditable software for sensitive public sector use.
How should governments evaluate a government messaging app for procurement?
Evaluation should cover five dimensions: legal architecture (data residency, GDPR Article 28 compliance, Cloud Act exposure), technical controls (E2EE, self-hosting, air-gap support, RBAC), auditability (open-source codebase, third-party security audits, audit log capability), operational resilience (ability to operate without vendor dependency, federated identity integration), and supply chain risk (vendor security posture, dependency on third-party infrastructure). Reviewing government messaging app options against these five dimensions provides a structured starting point for procurement evaluation.