Organizations in healthcare, finance, defense, energy, and government face a specific problem with internal communication: the tools most teams default to were not built for regulated environments. Secure internal communication platforms for regulated industries must satisfy compliance frameworks, support formal accreditation processes, and keep sensitive data within controlled infrastructure. Most commercial collaboration tools fail on at least one of these requirements.
The cost of getting this wrong is rising. IBM's 2025 Cost of a Data Breach Report found that healthcare breaches now average $7.42 million per incident, making it the most expensive sector for the 14th consecutive year. Financial services organizations spend an average of $6.08 million per breach, 22% above the global average. These figures reflect not just the breach itself but the regulatory fines, notification costs, and remediation that follow when communication tools lack proper governance.
01Why regulated industries cannot rely on standard collaboration tools
The core issue is architectural. Commercial SaaS platforms like Slack and Microsoft Teams assume vendor-controlled cloud infrastructure, persistent internet connectivity, and a one-size-fits-all compliance model. Those assumptions break down in environments where data cannot leave a specific jurisdiction, where formal accreditation is required before any tool is approved, or where operations continue in disconnected conditions.
Third-party risk compounds the problem. Verizon's 2025 Data Breach Investigations Report found that third-party involvement in breaches doubled year-over-year, reaching 30% of all confirmed breaches. When your messaging platform routes data through external servers you do not control, every message becomes a potential exposure point during a vendor breach.
Shadow IT makes this worse. Gartner estimates that 30 to 40% of enterprise IT spending goes to unapproved tools. In regulated industries, every unsanctioned messaging app is a compliance gap waiting to surface in an audit. Staff adopt consumer tools like WhatsApp or Telegram because approved alternatives are too slow to deploy or too limited in functionality. The result: sensitive conversations happening on platforms with no communication security controls, no audit trails, and no data retention policies.
02What compliance-ready secure internal communication actually requires
A platform being "secure" is not the same as being compliance-ready. Regulated industries need communication tools that can be evaluated, configured, and governed by the customer's own security team. Here is what that looks like in practice.
Data sovereignty and residency control
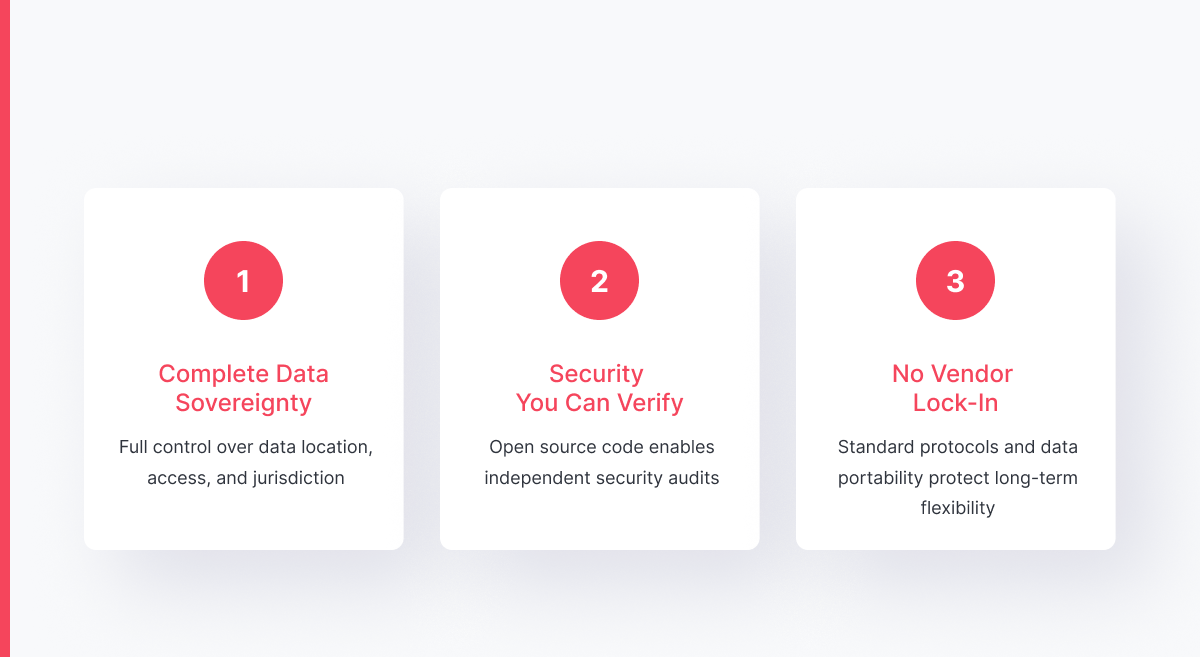
The platform must deploy on infrastructure the organization controls. This means on-premises, private cloud, sovereign cloud, or fully air-gapped environments. For organizations subject to GDPR, this is not optional. The Schrems II ruling makes data transfers to non-EU jurisdictions a legal risk. GDPR-compliant messaging requires that data stays where the organization's legal framework demands.
Granular access controls
Role-based (RBAC) and attribute-based (ABAC) access controls, integrated with existing identity providers through SSO, LDAP, and multi-factor authentication. In classified or compartmentalized environments, access must be enforced at the channel and message level, not just the platform level.
Audit logging and retention policies
Every message, file share, and administrative action must be logged and retrievable. Configurable retention policies let compliance teams enforce data lifecycle rules that match their regulatory framework, whether that is HIPAA's six-year retention requirement or NIS2's incident reporting obligations.
End-to-end encryption with customer-controlled keys
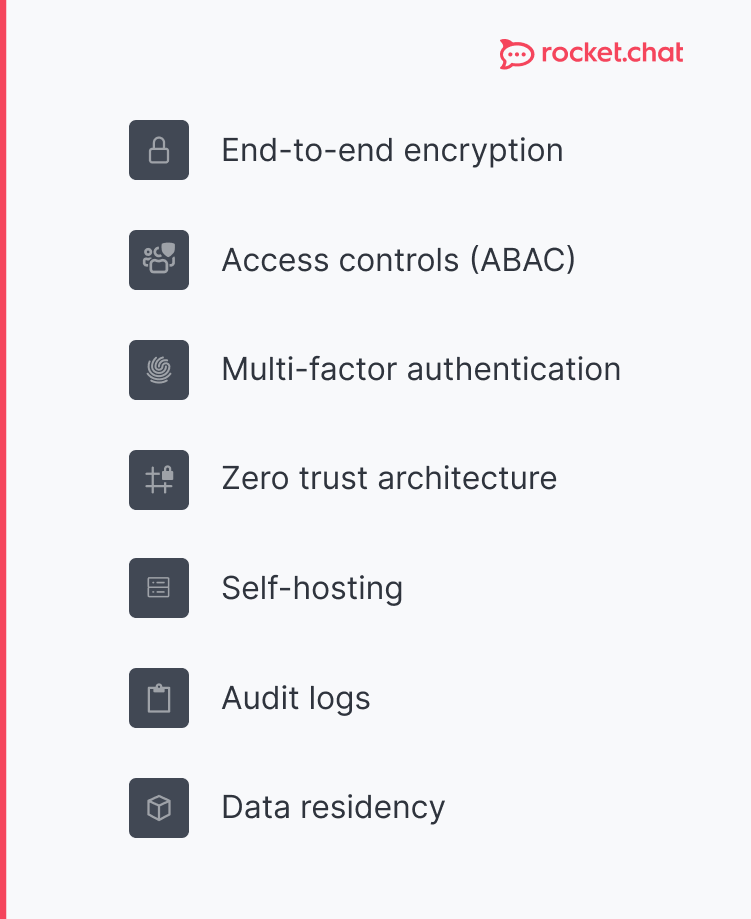
Encryption where the vendor holds the keys is encryption in name only. Regulated organizations need to manage their own key infrastructure so that no external party, including the platform vendor, can access message content. This is a baseline requirement for any secure team chat deployment in government or defense environments.
03How NIS2 changes the calculus for European organizations
The EU's NIS2 directive, now being enforced across member states, significantly expands which organizations must meet strict cybersecurity requirements. Energy, transport, banking, healthcare, water, digital infrastructure, and public administration all fall within scope. Non-compliant entities face fines of up to 10 million euros or 2% of global annual revenue, whichever is higher.
NIS2 requires organizations to implement measures for incident handling, supply chain security, and secure communications. For many organizations, this means their existing instant messaging platforms no longer meet the bar. The directive specifically addresses third-party risk management, which means the vendor dependency inherent in SaaS collaboration tools creates a compliance exposure that auditors will flag.
Organizations evaluating NIS2 compliance for their communication stack should prioritize platforms that support self-hosted deployment, provide full audit trails, and offer digital sovereignty by design rather than as an afterthought.
Note: NIS2 implementation timelines vary by member state. Organizations should consult legal advisors for jurisdiction-specific obligations.
04Self-hosted deployment: the foundation of secure internal communication
For regulated industries, the deployment model is not a technical preference. It is a compliance requirement. Self-hosted communication platforms give organizations complete control over where data resides, who accesses it, and how it is governed.
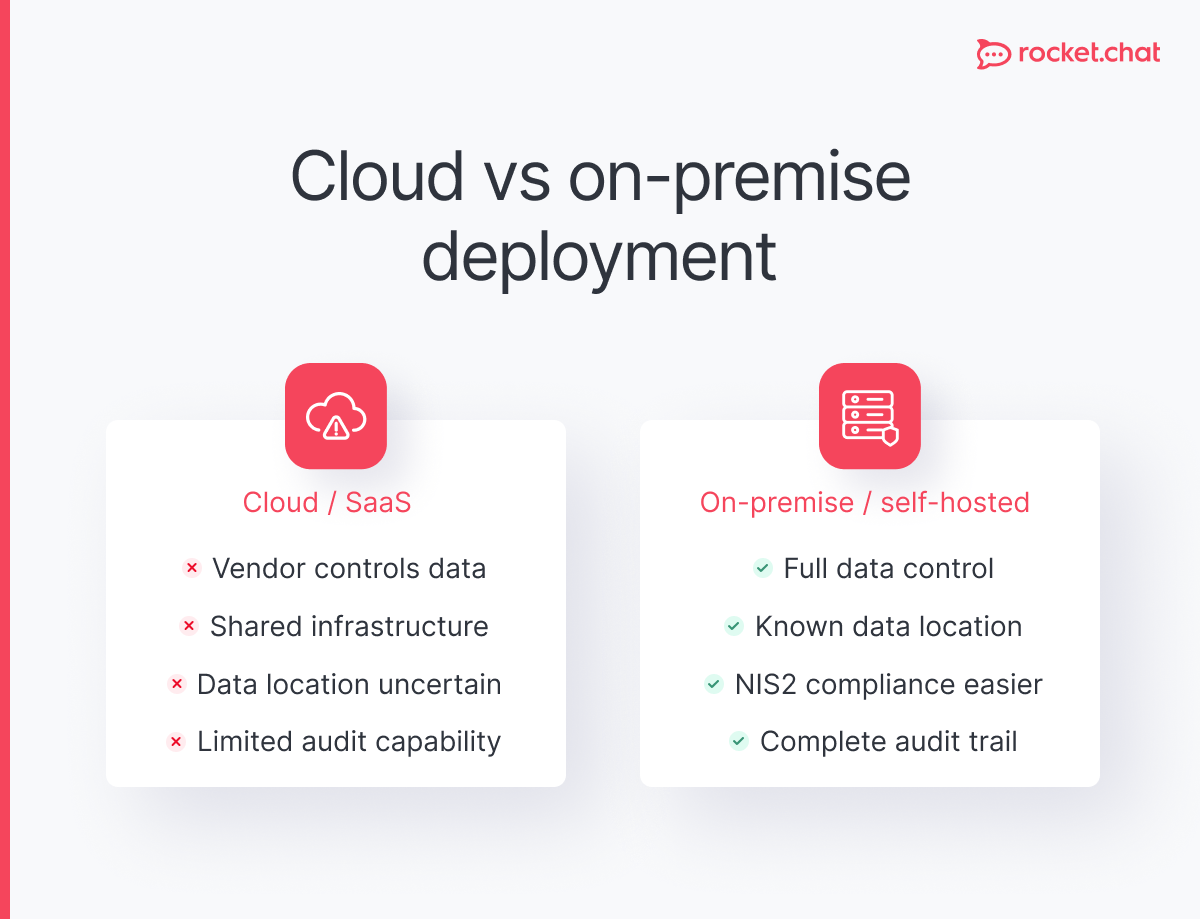
This matters most in three scenarios:
- First, organizations operating under data residency mandates, where government communication cannot leave national borders.
- Second, defense and intelligence environments requiring air-gapped deployments on classified networks.
- Third, critical infrastructure operators who need communications that function during network outages or cyberattacks, independent of any external cloud service.
A self-hosted chat deployment also simplifies the accreditation process. When the platform runs inside controlled infrastructure, security teams can assess, harden, and certify it against frameworks like NIST 800-53, ISO 27001, or national defense standards without negotiating access to a vendor's cloud environment.
Rocket.Chat supports deployment on-premises, in private cloud, in sovereign cloud environments, or fully air-gapped. It holds SOC 2 Type II attestation (achieved February 2026) and ISO 27001 certification, both independently audited. For U.S. defense, it supports ATO up to IL6 for classified deployments.
05Evaluating platforms: what to compare
Not every platform marketed as "secure" meets the requirements of regulated industries. The comparison below highlights the capabilities that matter for workplace communication in environments with formal compliance obligations.
| Capability | Consumer apps WhatsApp, Signal | SaaS platforms Slack, Teams | Secure open-source platforms Rocket.Chat |
|---|---|---|---|
| Self-hosted deployment | No | Limited or unavailable | Full support (on-prem, air-gapped, sovereign cloud) |
| Data residency control | Vendor-controlled | Vendor-controlled with limited region selection | Customer-controlled, any jurisdiction |
| End-to-end encryption with customer keys | Vendor-managed keys | Vendor-managed keys | Customer-controlled key management |
| Audit logging | None | Partial, plan-dependent | Comprehensive, configurable |
| RBAC/ABAC access controls | None | Basic RBAC | Granular RBAC and ABAC |
| Compliance certifications | None | SOC 2, ISO 27001 (vendor-held) | SOC 2 Type II, ISO 27001 (customer-verifiable) |
| Air-gapped operation | Not possible | Not possible | Fully supported |
| Federation across organizations | Not supported | Limited | Matrix-native, governed federation |
| Extensibility | None | Marketplace plugins | Apps Engine with scoped permissions |
| Open-source code audit | No | No | Yes, MIT license |
Consumer encrypted messaging apps solve a different problem. They protect individual conversations but provide no organizational governance, no audit trails, and no compliance support. They are not suitable for regulated use.
SaaS platforms offer collaboration features but depend on vendor infrastructure. For organizations where secure messaging requires sovereignty and formal accreditation, that dependency is a disqualifier.
Open-source, self-hosted platforms like Rocket.Chat give regulated organizations what neither category can: full infrastructure control, auditable code, and the flexibility to meet sector-specific compliance requirements. The most secure messaging approach for regulated industries combines self-hosted deployment with open-source transparency.
For European organizations evaluating alternatives to US-controlled SaaS tools, understanding the sovereign alternatives available is a practical first step. Government buyers specifically should assess government messaging platforms against their procurement frameworks and accreditation requirements. Organizations still running legacy Microsoft on-premises infrastructure can explore Teams alternatives designed for high-assurance environments.
Frequently asked questions
What are secure internal communication platforms for regulated industries?
Secure internal communication platforms for regulated industries are collaboration tools designed to meet the compliance, data residency, and security requirements of sectors like healthcare, finance, defense, energy, and government. Unlike consumer messaging apps or standard SaaS tools, these platforms support self-hosted deployment, provide granular access controls, offer comprehensive audit logging, and enable customer-controlled encryption. They are built to pass formal security reviews and support accreditation processes required by frameworks such as HIPAA, GDPR, NIS2, and NIST 800-53.
Why can't regulated industries use standard messaging tools like Slack or Microsoft Teams?
Standard SaaS messaging platforms store data on vendor-controlled cloud infrastructure, which conflicts with data residency mandates, sovereignty requirements, and formal accreditation processes in regulated sectors. These platforms do not support air-gapped deployment, do not offer customer-controlled encryption key management, and provide limited audit capabilities. For organizations subject to HIPAA, GDPR, NIS2, or defense-grade security standards, the lack of infrastructure control makes standard tools a compliance liability rather than a productivity gain.
How does self-hosted deployment improve compliance for internal communication?
Self-hosted deployment gives the organization complete control over where data resides, who can access it, and how it is governed. This eliminates vendor dependency for data residency, allows security teams to harden the environment to their own standards, and simplifies formal accreditation because the entire platform runs within infrastructure the organization already certifies and monitors. It also ensures communications remain operational during network outages or cyberattacks, independent of any external cloud service.
What compliance frameworks require secure internal communication platforms?
Multiple regulatory frameworks impose requirements that affect internal communication tools. HIPAA requires access controls, audit trails, and encryption for electronic protected health information. GDPR and Schrems II restrict the transfer of personal data outside the EU and require demonstrable data protection measures. NIS2 mandates incident handling, supply chain security, and secure communications for essential and important entities across the EU. NIST 800-53 and NIST 800-171 set security control baselines for U.S. federal systems and defense contractors. Each framework has specific technical requirements that general-purpose collaboration tools are not designed to satisfy.
What is the difference between encrypted messaging and compliance-ready communication?
Encryption protects message content in transit and at rest, but compliance-ready communication goes further. It includes configurable data retention policies, comprehensive audit logging of all user and administrative actions, role-based and attribute-based access controls, integration with enterprise identity providers, and the ability to deploy on customer-controlled infrastructure. A platform can encrypt messages while still failing compliance requirements if it lacks governance, auditability, or data residency controls. Regulated industries need both encryption and the full governance framework around it.
How does open-source transparency benefit regulated organizations?
Open-source platforms allow regulated organizations to inspect the full source code, verify security claims independently, and audit the platform against their own standards rather than relying on vendor attestations. This is particularly valuable during formal accreditation processes, where security teams need to validate exactly how data is handled, stored, and protected. An MIT-licensed platform like Rocket.Chat also eliminates AGPL licensing complications that can create legal friction in government and defense procurement.
What should regulated industries prioritize when evaluating secure communication platforms?
The five most critical evaluation criteria are: deployment flexibility (on-premises, sovereign cloud, and air-gapped support), data residency and sovereignty controls, compliance certification evidence (independently audited SOC 2 Type II, ISO 27001), extensibility through a governed framework rather than unrestricted plugins, and federation capabilities for secure cross-organization collaboration. Cost and user experience matter, but in regulated environments, these factors are secondary to compliance posture and infrastructure control.