Today we released a hotfix for the Rocket.Chat desktop client.This fixes some vulnerabilities found on Chrome (CVE-2017-5124) and Electron (CVE-2018-1000006).We urge users to update their Rocket.Chat desktop client to the latest version as these bugs can be exploited for remote code execution which can result in stolen data and system compromise.If you are a developer and maintain a forked version of Rocket.Chat please ensure to update your dependencies.Please consult Rocket.Chat.Electron for more information.If you have any questions, concerns or require advice please contact security@rocket.chat or chat to us on https://open.rocket.chat/channel/support.Special thanks to rmetzler for reporting both vulnerabilities found in the Rocket.Chat repository.
← All posts
Electron 2.10.2 hotfix release
Keep reading
Related posts.
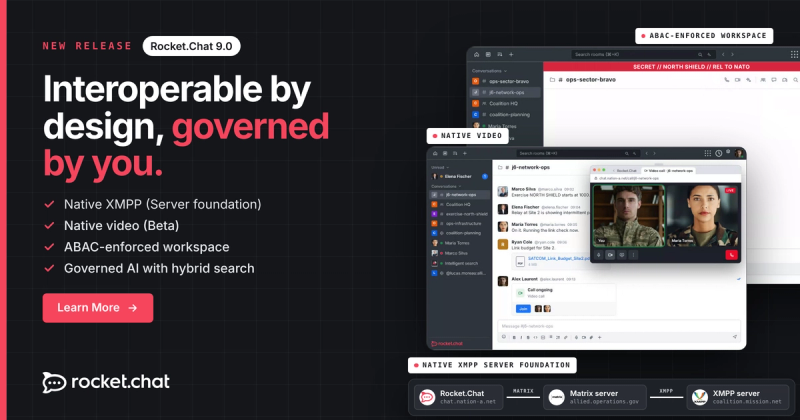 Rocket.Chat 9.0: Interoperable by design, governed by youRocket.Chat 9.0 makes interoperable by design real: a native XMPP server foundation alongside native Matrix, so you and your partners can connect whatever protocol each side runs, without giving up governance or control. Native video completes the real-time comms bundle, and the ABAC-enforced workspace puts every channel inside the access boundary.Read article →9 min read
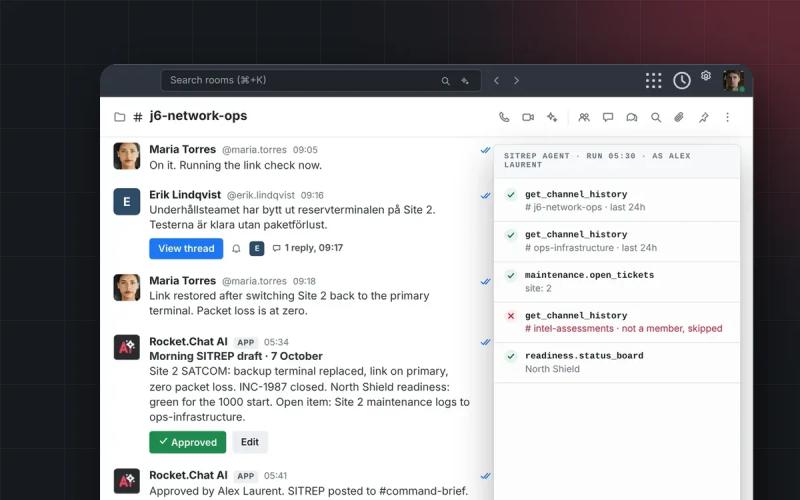 Rocket.Chat 8.8 introduces native MCP server for AI agentsConnect any MCP-compatible AI agent to your workspace without custom code, plus private channels encrypted by default.Read article →5 min read
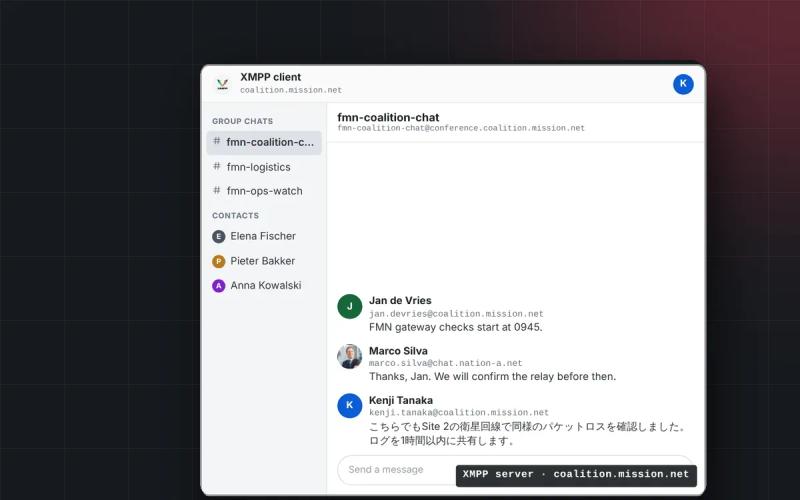 Rocket.Chat 8.7 brings XMPP interoperability for coalition operationsFederate with XMPP coalition partners on FMN networks from the same platform your teams use every day.Read article →5 min read