01The core problem: who controls your communications infrastructure?
Digital sovereignty, in its most operational definition, is the ability to guarantee that no external government, corporation, or court can compel access to your data without your knowledge and consent. For European governments and critical infrastructure operators, that guarantee is increasingly difficult to make when core communication tools operate under legal frameworks that sit outside EU jurisdiction.
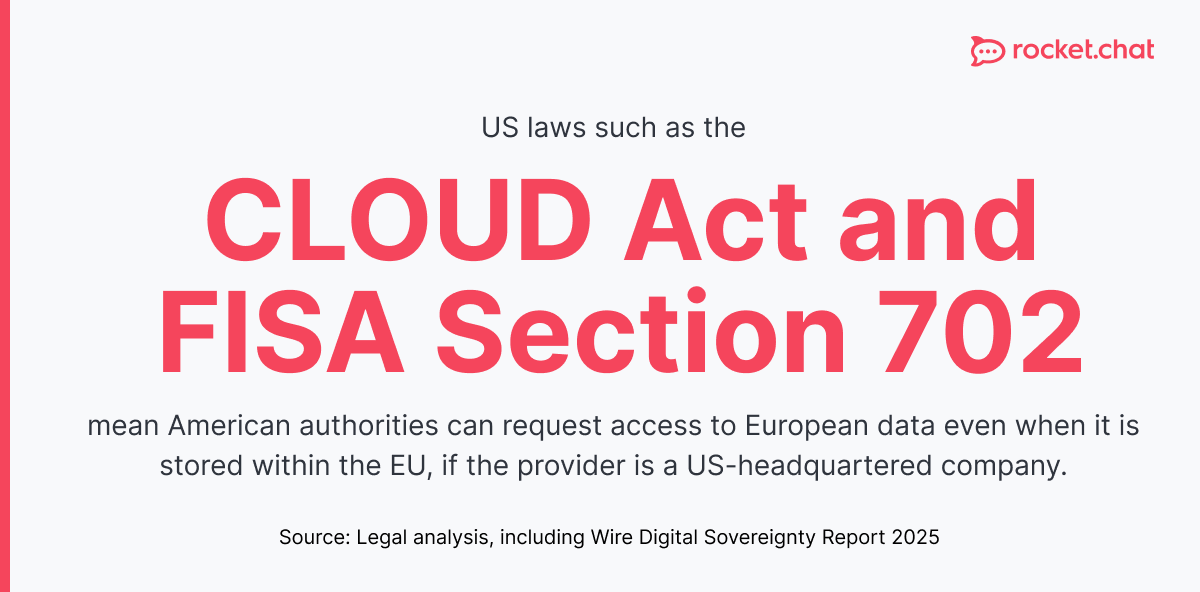
The legal tension is concrete. The US CLOUD Act (2018) requires American companies to provide data to US law enforcement regardless of where that data is stored. This creates a direct conflict with EU data protection law and, more critically, with the security posture of any public sector body handling sensitive or classified information. A European ministry using Microsoft Teams or Slack is not, by default, operating a sovereign communications environment, even with data residency configured to EU regions.
This distinction matters as the infrastructure landscape evolves. AWS has launched a European Sovereign Cloud designed to give EU customers operator-level isolation from AWS personnel and US legal processes. That is a meaningful architectural step.
But sovereign suitability is not a binary determined by vendor nationality. It is determined by whether the deploying organisation can fully audit, control, and if necessary, isolate its communications infrastructure. A tool built by a US company but deployed self-hosted on EU-controlled infrastructure, with customer-held encryption keys and no vendor network dependency, may provide stronger sovereignty guarantees than a "European sovereign cloud" offering where the vendor still manages access and keys.
The European Commission has acknowledged the underlying risk directly. Its 2030 Digital Compass sets explicit targets for digital infrastructure resilience, and the ENISA threat landscape consistently identifies supply chain compromise and espionage via commercial platforms as top-tier threats to public sector bodies.
Operational security failures increasingly trace back to commercial communication platforms. Metadata exposure, subpoena-accessible logs, and misconfigured cloud tenants remain primary vectors for intelligence collection against government targets.
02What EU digital sovereignty actually requires in practice
EU digital sovereignty is often discussed at the policy level, but the operational requirements are specific. For public sector and critical infrastructure bodies, sovereignty across communications infrastructure means:
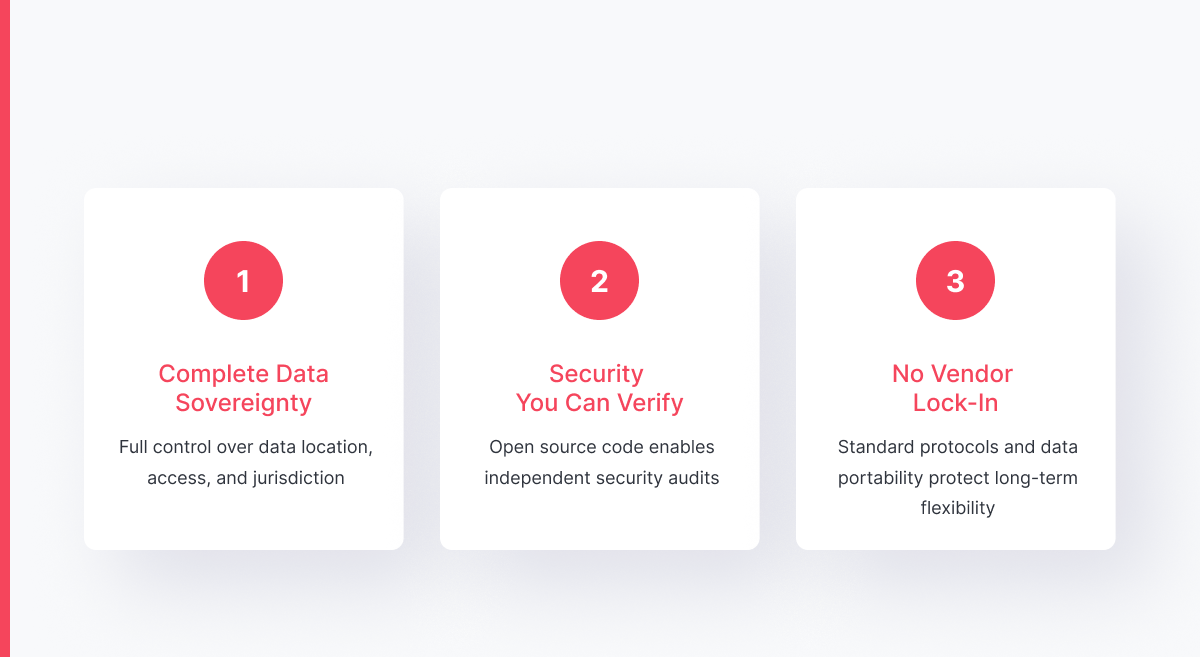
- Full data ownership. Organisations must be able to deploy, operate, and audit their communication platforms on infrastructure they control entirely. This means on-premises deployment or sovereign cloud providers, not shared tenancies where a vendor retains administrative access under a foreign legal framework.
- End-to-end encryption with key custody. Encryption is only sovereign when the organisation holds the encryption keys. Platforms that manage keys on behalf of the customer provide no protection against legal compulsion or insider access by the vendor. Explore what end-to-end encrypted messaging means in practice for regulated environments.
- Air-gap capability. For defence, intelligence, and critical national infrastructure, the ability to operate in fully disconnected environments is a baseline requirement. Air-gapped collaboration eliminates the attack surface of internet-connected SaaS platforms entirely.
- Compliance with EU regulatory frameworks. NIS2, GDPR, and sector-specific regulations impose data handling obligations that are structurally incompatible with certain hyperscaler architectures. NIS2 compliance requirements, for example, mandate incident reporting, risk management, and supply chain security controls that require clear visibility into infrastructure. That visibility is often opaque in SaaS deployments.
- Open-source auditability. Closed-source platforms cannot be independently verified. For high-assurance environments, source code auditability is a prerequisite for deployment approval.
03European technological sovereignty and digital infrastructure: the regulatory push
The EU's legislative programme over the past five years represents the most sustained regulatory effort to define and enforce digital sovereignty requirements since the formation of the single market. The cumulative effect is significant.
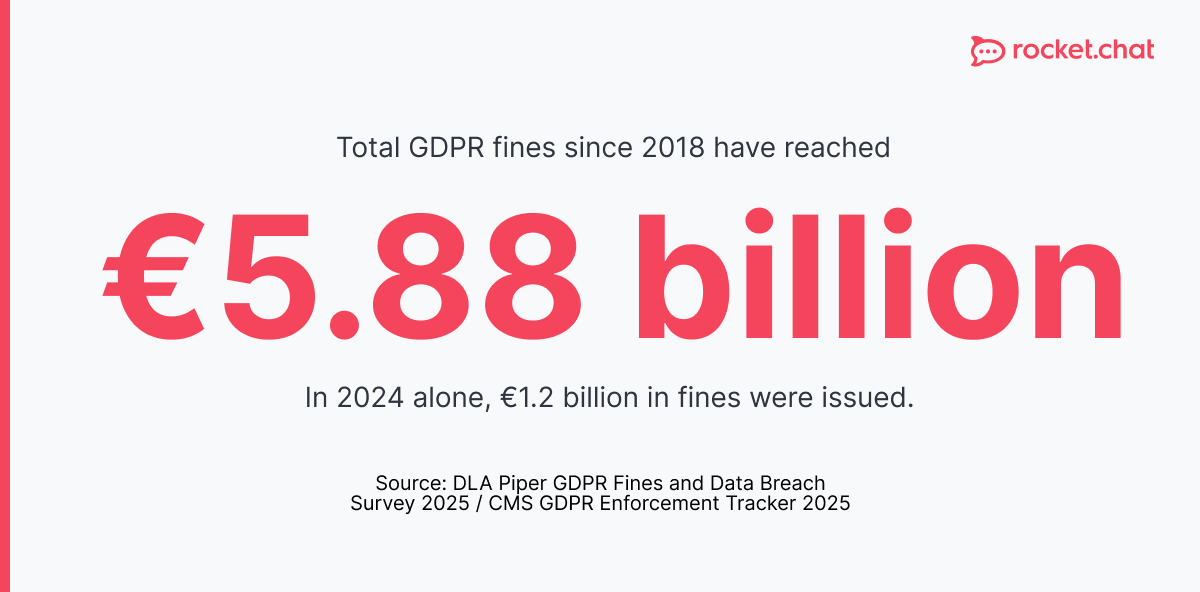
GDPR established that personal data of EU residents must be handled according to EU law, and that transfers to third countries require adequate protection. The Schrems II ruling in 2020 invalidated the EU-US Privacy Shield, creating ongoing uncertainty for organisations relying on US-headquartered vendors where the vendor, rather than the customer, controls data access. GDPR-compliant messaging is now a compliance baseline, not a differentiator.
NIS2 extended security obligations to a much wider set of critical infrastructure sectors and imposed stricter requirements on supply chain risk management. Operators of essential services cannot delegate security accountability to vendors without contractual and technical controls that many commercial platforms do not support.
The Cyber Resilience Act extends the sovereignty logic into software supply chains. The direction of regulatory travel is clear: the EU requires organisations to demonstrate verifiable control over their technology stack, regardless of where that technology originates.
A tool’s country of origin is not the determining factor. What matters is whether the deploying organisation can fully audit it, self-host it, hold its encryption keys, and operate it without ongoing dependency on the vendor’s infrastructure.
The European sovereign cloud and Microsoft Teams alternatives conversation is now mainstream in public sector procurement. Several member states, including France, Germany, and the Netherlands, have published guidance or mandates requiring public bodies to assess communication platform sovereignty based on architectural criteria, not vendor nationality.
04The communication layer as a sovereignty risk surface
Among all digital infrastructure layers, real-time communication platforms represent an acute and underappreciated sovereignty risk. Governments and defence organisations routinely conduct sensitive operations, coordinate incident response, and share classified information over platforms architected for commercial users.
The risk profile of commercial SaaS communication tools includes:
- Metadata exposure. Even where message content is encrypted, metadata about who communicated with whom, when, from where, and for how long is often logged, retained, and accessible to the vendor. For intelligence and defence contexts, metadata is itself operationally sensitive.
- Vendor access to keys. Most commercial platforms retain administrative access sufficient to decrypt communications if compelled. This is incompatible with secure team communication requirements in government and defence contexts.
- Dependency on foreign incident response. When a commercial platform is breached, the response timeline, scope of disclosure, and remediation are controlled by the vendor, not the customer. For critical infrastructure operators, this is an unacceptable loss of control.
- Integration with foreign intelligence supply chains. Cloud platforms operated by US companies are subject to Foreign Intelligence Surveillance Act (FISA) orders, which are issued without notification to the target and cannot be disclosed by the vendor. No contractual control can mitigate this risk.
Reviewing secure collaboration tools specifically designed for high-assurance environments shows the gap between commercial defaults and sovereign requirements is significant, but bridgeable.
05Sovereign communication: what the architecture looks like
A genuinely sovereign communication environment for government or critical infrastructure is defined by deployment model, not by vendor nationality alone. The key architectural requirements are:
- Self-hosted deployment on controlled infrastructure. The platform runs on hardware and virtualisation infrastructure that the organisation owns or operates directly. This includes on-premises deployments, classified facilities, and sovereign cloud environments where the operator has contractual and technical isolation from the cloud provider's personnel and legal exposure.
EU-based national cloud providers and AWS European Sovereign Cloud, which is designed to give customers operator-level isolation from AWS staff and US legal processes, both qualify under this model provided the remaining architectural controls (key custody, audit ownership, network isolation) are also met. What disqualifies a deployment is not the cloud model itself, but any residual vendor access that the organisation cannot revoke.
- Customer-held encryption keys. The organisation generates, stores, and rotates encryption keys without vendor involvement. This is distinct from "bring your own key" (BYOK) schemes where the vendor still processes data under the key. True key custody means the vendor cannot access plaintext under any circumstances.
- Federated identity and access management. Authentication is controlled by the organisation's own identity infrastructure, with no dependency on vendor-managed identity providers that could be revoked or compromised.
- Full auditability. Audit logs are owned by the organisation and cannot be modified or deleted by the vendor. This supports both internal compliance and forensic investigation. Understanding organisational security architecture is essential for specifying these controls accurately.
- Network isolation capability. For the highest-sensitivity environments, the platform must be operable with no external network connectivity: no DNS resolution to vendor infrastructure, no telemetry, no automatic updates. Government chat and military communication requirements often specify this as mandatory.
06Comparing sovereignty postures: commercial SaaS vs self-hosted open-source
The following table compares the sovereignty characteristics of the dominant commercial communication platforms against a self-hosted open-source deployment model relevant to European government and critical infrastructure contexts.
| Requirement | Microsoft Teams EU tenant | Slack Enterprise Grid | Self-hosted open-source |
|---|---|---|---|
| Data residency in EU | Yes | Yes | Yes |
| Customer-held encryption keys | Partial (BYOK, vendor processes) | No | Yes |
| Air-gap / offline deployment | No | No | Yes |
| Source code auditability | No | No | Yes |
| US CLOUD Act exposure | Yes (US parent) | Yes (US parent) | No (EU infra) |
| FISA order risk | Yes | Yes | No |
| NIS2 supply chain control | Limited | Limited | Yes |
| On-premises deployment | Limited | No | Yes |
| Full audit log ownership | No | No | Yes |
07The path forward for European institutions
European governments are not starting from zero. France's SecNumCloud certification scheme, administered by ANSSI, already mandates that public sector bodies use cloud providers meeting strict sovereignty and data isolation standards. Germany's Sovereign Tech Fund invests in the open-source foundations — encryption tools, protocols, and core libraries — that sovereign communication deployments depend on. These are concrete, operational programmes, not aspirational ones.
For senior decision-makers, the practical implication is that digital sovereignty in communications is not a future state. It is an available architecture today. The question is one of procurement will, vendor selection, and organisational change management, not technical feasibility.
Reviewing the landscape of encrypted messaging apps built for regulated industries, government messaging apps, and the broader government communication technology market shows a maturing set of sovereign-ready options. The cost of inaction is continued exposure to foreign legal compulsion, supply chain risk, and regulatory non-compliance. That cost now outweighs the cost of migration.
European institutions that treat communication sovereignty as a near-term operational priority, rather than a long-term strategic aspiration, will be better positioned to meet both regulatory obligations and the security demands of an increasingly contested threat environment.
For organisations evaluating instant messaging platforms or chat platforms against sovereign requirements, the most secure options are those that combine open-source auditability with self-hosted deployment and customer-controlled encryption. A detailed comparison of the most secure messaging apps available for government use cases confirms that architecture, not geographic origin, determines sovereign suitability.
Organisations evaluating a sovereign Slack alternative for Europe should apply the architectural checklist above as a procurement filter, not vendor assurances or data residency certificates alone.
Frequently asked questions
What is digital sovereignty and why does it matter for European governments?
Digital sovereignty is the capacity of a government or organisation to control its own digital infrastructure, data, and services without dependence on foreign technology providers subject to non-EU legal jurisdiction. It matters for European governments because US cloud providers operating under the CLOUD Act and FISA can be compelled to disclose data held on behalf of EU public bodies, regardless of where that data is physically stored. This creates a structural conflict with EU data protection law and with the security requirements of any body handling sensitive or classified information.
How does EU digital sovereignty differ from data residency?
Data residency means that data is stored within the borders of a specific jurisdiction, but it does not guarantee that foreign entities cannot access that data. A US company storing data in a Frankfurt data centre is still subject to US law, including orders that require disclosure to American authorities without notifying the EU customer. True digital sovereignty requires that the organisation controls not just where data is stored, but who can access it, under what legal framework, and with what technical controls, including encryption key custody and deployment independence from the vendor.
What regulations are shaping European technological sovereignty?
The primary regulatory drivers are the GDPR, which restricts data transfers to third countries and requires adequate protection for EU personal data; the NIS2 Directive, which extends security obligations to critical infrastructure operators and includes supply chain risk requirements; and the EU Cyber Resilience Act, which imposes security requirements on software and hardware products placed on the EU market. Together, these create a compliance environment that is structurally incompatible with unrestricted use of US hyperscaler platforms for sensitive public sector workloads.
What does a sovereign communication platform look like in practice?
A sovereign communication platform for government or critical infrastructure use is self-hosted on infrastructure controlled by the organisation, uses end-to-end encryption with keys held exclusively by the organisation, supports air-gapped deployment for the highest-sensitivity environments, and is built on auditable open-source code. Critically, vendor origin does not determine sovereignty. A platform developed outside Europe can fully meet sovereign requirements if it is self-hosted on EU-controlled infrastructure, operates without ongoing vendor network dependency, and gives the deploying organisation complete control over keys, logs, and updates. What disqualifies a platform is not where it was built, but whether the vendor retains any privileged access that cannot be revoked.
How does the US CLOUD Act affect European public sector organisations using US software?
The CLOUD Act (Clarifying Lawful Overseas Use of Data Act, 2018) requires US companies to provide data to US law enforcement and intelligence agencies upon request, even when that data is stored outside the United States. For European public sector bodies using Microsoft Teams, Slack, Google Workspace, or other US-headquartered platforms, this means their communications and data could legally be accessed by US authorities without the knowledge or consent of the EU organisation or its member state government. No contractual data protection addendum can override this statutory obligation.
What is the relationship between NIS2 compliance and digital sovereignty?
NIS2 requires operators of essential services and important entities to implement risk management measures that include supply chain security, access controls, encryption, and incident handling. These requirements implicitly demand sovereignty-aligned architecture: organisations cannot demonstrate adequate supply chain control if their communications infrastructure is operated by a vendor over whom they have limited contractual leverage and no ability to audit. NIS2 also requires that organisations can respond to incidents rapidly and with full access to their own logs and data. Self-hosted sovereign platforms provide these capabilities by design; SaaS platforms often constrain them.
Which European sectors face the highest digital sovereignty risk from non-sovereign communication tools?
Defence and intelligence services face the highest risk, as any metadata or content exposure can have direct operational consequences. Critical national infrastructure operators in energy, water, transport, and financial services face both regulatory and operational risk: a compromised communication platform can be used to coordinate or execute attacks on physical infrastructure. Central and local government bodies face legal risk from GDPR and NIS2 non-compliance, as well as reputational risk from exposure of citizen data or policy deliberations. Healthcare organisations handling sensitive patient data and law enforcement agencies with operational security requirements are also in the high-risk category.